 ipSpace.net blog
Author Archives: ipSpace.net blog
ipSpace.net blog
Author Archives: ipSpace.net blog
My initial “configuring Arista cEOS with Netmiko or Ansible” test was a bit biased. netlab generates the final configuration snippets in both cases (due to Ansible FUBARs we had to deal with), but then Netmiko just sends the configuration commands to the switch (after entering configuration mode), while the Ansible eos_config module executes show running, identifies the difference, and sends only the changes to the device.
While that use case is highly relevant (after all, we’re configuring network devices ;) I really should have done an apples-to-apples comparison, and FRRouting virtual machines are the ideal playground.
Now that we know what we need to make layer-3 services (BGP-free core transporting IPv4 and IPv6 traffic) work with SRv6, let’s go through the steps needed to configure them on Junos, continuing from the baseline SRv6 with IS-IS configuration (and again relying on the excellent SRv6 Micro-SID (uSID) Basics article1 by Krzysztof Szarkowicz).
In the BGP-Free Network Core with SRv6, we identified the components we need (assuming IBGP+IGP design):
I decided to make Netmiko the default configuration deployment method netlab uses for Cisco IOS XR. It works great, and I don’t have to worry about whether the user runs IOS XRd control-plane (in which case scripts work) or vRouter (in which case there’s a VM inside the container, so no luck).
After fixing the initial glitches (more on that another time), all integration tests passed except the OSPFv2 default origination test. It turns out the default waiting time (30 seconds) is way too low; Cisco IOS XR needs almost 90 seconds (after its reboot completes) to originate the OSPFv2 default route.
With the growing number of SRv6 implementations that netlab supports, it made sense to create a set of topologies to help you get started exploring the SRv6 world. The sample topologies include:
Read the getting started document and have fun exploring the scenarios 😎
We launched device configuration with Netmiko in the September 2026 netlab release and made it easier to use in the October 2026 release. It will become the default configuration method for several popular platforms (Arista EOS, Cisco IOS, Cisco Nexus OS, Cisco IOS XR, FRRouting virtual machines) in a few months, but before doing that, I wanted to check whether the change matters.
TL&DR: Yes, it does.
The Network Automation Forum is running the annual State of Network Automation Survey (here are the 2025 results).
If you’re involved in network automation in any way (I hope you are), please take a few minutes and complete it. Thank you!
The concept of a BGP-free core is decades old:
TL&DR: It’s really hard to figure out when a Cisco IOS box configured via its CLI reports a configuration error.
One of the drawbacks of using Netmiko to configure network devices is its inherent lack of error detection – while it can switch into configuration mode and exit it (including a commit operation if needed), it doesn’t detect configuration errors.
No big deal (I thought); the configuration error messages generated by Cisco IOS always start with a percent sign (%), so I’d just use that as the error_pattern parameter of the send_config_from_file command. A few integration test failures later, that turned out to be a bad idea; Cisco IOS starts errors and warnings with the percentage sign, and there’s absolutely no reliable way to differentiate between the two.
netlab release 26.10 adds new SRv6 implementations and features:
Other new features include:
Chris Siebenmann publishes articles written from an interesting perspective: he’s a Unix herder at a university (based on my ancient, similar experience, that’s usually worse than herding cats).
In one of his recent articles, he applied the desire paths ideas to IT: don’t fight how people are doing things; either kindly nudge them in the right direction, or help them get stuff done the way they like to get it done, but in the least harmful way. I could definitely use some of his wisdom decades ago 🤷🏻♂️.
I wanted to make my SRv6 lab examples usable with more platforms. Adding netlab Junos SRv6 support (included in the 26.10 release) was relatively easy; here’s what I learned while working on the pull request:
Andre Toonk published yet another Internet-measuring tool: watchthenet.com tries to ping every IPv4 address every few hours (probing every /24 every 49 seconds), resulting in a rapidly updated state of the Internet. If an ISP has a bad hair day, Andre knows within minutes.
Make sure you bookmark his website and read his blog post for more details.
When I implemented prefix filters in netlab (release 1.9.0), I wanted them to match the final device configurations as closely as possible, including the one prefix per entry rule to match the device configuration sequence numbers. That worked well, but resulted in YAML bloat, since each matching prefix requires several lines of YAML.
We tried to use the same approach with ACLs but quickly gave up when we realized the port not in range operation requires multiple ACL entries on most platforms. With the matching sequence numbers paradigm gone with the wind, it made no sense to limit ourselves to one prefix per ACL entry – the initial ACL entry implementation already accepted lists of prefixes and expanded them into ACL entries.

The 5-hour Reliability Theory: Networking through a Systems Analysis Lens webinar by Rachel Traylor is now available without a valid ipSpace.net account. Enjoy!
To watch more free ipSpace.net videos, browse them here, or click the Access Free Content button in any webinar roadmap.
netlab release 26.09 added support for Syslog clients and servers. We implemented the clients on numerous platforms; the only Syslog server implementation is the dnsmasq container.
Adding Syslog to a netlab lab is (almost) trivial:
The OSPF is stuck in database exchange state symptom is probably familiar to every networking engineer who ever had to pass a certification exam. It’s caused by the MTU mismatch between adjacent OSPF routers.
The recent (unexpected) trip into the how crazy is it to declare your interface MTU to be zero wonderland uncovered way more than I ever wanted to know about this arcane topic. Here are a few highlights (thanks a million to Aleksey Popov for researching this topic and posting information here, here, and here).
After a long journey, we finally we got to the final scenario in my ITNOG10 Segment Routing workshop: EVPN services over an SR-MPLS core.
I used the same lab topology as in the previous services-focused scenarios blog post, replacing two PE-to-host subnets with a stretched VLAN.
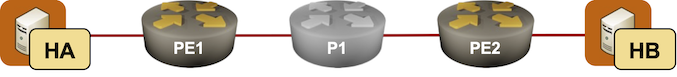
EVPN over SR-MPLS core
netlab release 26.09 brings more network services goodies:
Other new features include:
When I started the netlab project, Vagrant was the go-to tool if you wanted to build a virtual environment described in a text configuration file (an idea popularized as infrastructure-as-code). It wasn’t ideal for what we were doing, but a tool rarely does a great job when used far away from its intended use case.
netlab initially supported Vagrant with VirtualBox, quickly adding support for KVM/libvirt through the vagrant-libvirt plugin. Life was good… until it wasn’t.
TL&DR: Badly. The vagrant-libvirt plugin mysteriously crashes when an existing virtual network (with a different libvirt name) uses the same IP subnet as the desired management network.
Background: netlab is using the vagrant-libvirt plugin to manage libvirt/KVM virtual machines with Vagrant. As I already have that infrastructure, I use it to start standalone virtual machines (usually to test various Ubuntu releases) on my Linux server. Things work great… until they don’t.
Here’s how I managed to waste half a day chasing imaginary gremlins caused by a simple error.