Deno is joining Cloudflare
The Deno team is joining Cloudflare to radically simplify self-hosting Workers and Durable Objects so developers can use the same primitives in more places.
For what this means and how it came about, here’s the story from Ryan Dahl, Senior Principal Engineer, and Kenton Varda, Distinguished Engineer.
Netmiko vs Ansible: Does It Matter?
We launched device configuration with Netmiko in the September 2026 netlab release and made it easier to use in the October 2026 release. It will become the default configuration method for several popular platforms (Arista EOS, Cisco IOS, Cisco Nexus OS, Cisco IOS XR, FRRouting virtual machines) in a few months, but before doing that, I wanted to check whether the change matters.
TL&DR: Yes, it does.
Hedge 322: AI Crash
Just about everyone is watching the financial markets, either wondering how much better they can get, or when the AI financing bubble is going to crash. Dough Dawson, from POTs and PANs, joins Tom and Russ to talk about the logic of a coming crash, and consider where engineers should be looking for potential future career fields to weather the storm.
download
WWE 2K26: Cara Efektif Mengatur Serangan dan Counter Gulat
Dalam dunia gim gulat yang terus berkembang, WWE 2K26 menawarkan pengalaman bermain yang semakin realistis dan dinamis. Bagi para penggemar game ini, menguasai teknik serangan dan counter dalam pertandingan gulat merupakan kunci untuk memenangkan pertarungan di dalam ring. Artikel ini akan membahas secara lengkap cara mengatur serangan dan counter di WWE 2K26, sehingga kamu dapat memaksimalkan performa dan strategi bermain pada periode terbaru ini.
Pendahuluan
WWE 2K26 hadir dengan berbagai peningkatan dari versi-versi sebelumnya, khususnya dalam hal mekanisme pertarungan dan interaksi antara pemain dengan AI maupun pemain lain secara online. Kemampuan untuk mengatur serangan dan counter kini jauh lebih kompleks dan menantang. Fokus utama dalam artikel ini adalah bagaimana kamu dapat mengoptimalkan penggunaan sistem serangan dan counter untuk mendominasi pertandingan, baik dalam mode single player maupun multiplayer online.
Mekanisme Serangan Dasar di WWE 2K26
Salah satu aspek terpenting saat bermain WWE 2K26 adalah memahami dasar-dasar serangan. Serangan dasar dapat dibagi menjadi dua jenis utama: serangan ringan dan serangan berat. Serangan ringan (light attack) biasanya cepat dan memiliki risiko lebih kecil untuk di-counter, sementara serangan berat (heavy attack) memberikan damage besar tapi lebih mudah diprediksi dan di-counter oleh lawan.
Pengaturan serangan di WWE 2K26 menuntut pemain untuk mengkombinasikan kedua jenis serangan Continue reading
NFS Underground 2: Cara Modifikasi Mobil dan Kuasai Balapan Jalanan
Dalam dunia game balap jalanan, NFS Underground 2 tetap menjadi salah satu judul paling ikonik yang mampu memikat pemain di seluruh dunia. Hingga saat ini, game ini masih populer di kalangan penggemar balap dan modifikasi mobil, terutama karena fitur kustomisasi yang mendalam dan gameplay yang seru. Artikel ini hadir untuk membahas secara lengkap cara memodifikasi mobil dan tips menguasai balapan jalanan di NFS Underground 2, sehingga Anda bisa mendapatkan pengalaman bermain yang maksimal di periode terbaru.
Mengenal Kelebihan NFS Underground 2 Dalam Dunia Balap Jalanan
NFS Underground 2 menawarkan kebebasan luar biasa dalam memilih dan memodifikasi jenis mobil favorit, yang menjadi daya tarik utama game ini. Dengan lingkungan kota yang luas dan variasi tantangan balapan yang beragam, Anda bisa menikmati berbagai mode yang menuntut kemampuan manuver, kecepatan, dan strategi dalam memodifikasi kendaraan.
Fitur modifikasi yang komprehensif memungkinkan pemain menyesuaikan aspek visual dan performa mobil, mulai dari cat body, decal, hingga tuning mesin dan suspensi. Hal ini memberikan peluang unik untuk mengoptimalkan mobil sesuai gaya balapan Anda, entah itu mengutamakan kecepatan puncak, akselerasi, atau handling di tikungan.
Cara Memodifikasi Mobil di NFS Underground 2
Modifikasi mobil dalam NFS Underground 2 tidak hanya sekadar mempercantik tampilan, namun juga meningkatkan performa guna Continue reading
Bridging technical depth and usability: The story behind Radar’s redesign
Radar provides a real-time view into global Internet trends, powered by Cloudflare’s global network. We support Cloudflare’s mission to help build a better Internet by making web data visible, clear, and actionable for everyone. Since launching in 2020, Radar has found a natural audience amongst expert users with technical backgrounds, such as network operators and academic researchers who rely on Radar data to observe industry trends and global events.
But Radar also has the potential to be a more regular, self-serve resource for journalists, human rights advocates and policymakers, and everyday users. Making Radar accessible to a wider audience is a core part of our vision, so we knew it was time to reevaluate the user experience: How could we make Radar more approachable to broader audiences, while preserving the depth and rigor that we currently have?
In this blog post, we’ll introduce the redesigned Radar, share our design process, and outline our broader vision for the platform’s future.
Challenges with the previous design
While the previous landing page was successful at showing the breadth of Radar’s data, the way that information was presented made it difficult to parse. The bento box layout gave everything similar visual weight, the Continue reading
Rolling the Root Key – Update
This is an update to an article I posted in May of this year. As I write this, it's now the 8th October, and the Root Key of the DNS is scheduled to roll on the 11th October. The major addition to this update is a list of vulnerable ISP networks which are showing a KSK Sentinel signal that they have not added to their DNS resolver's trusted key set at the end of this article.Please Respond: State of Network Automation Survey
The Network Automation Forum is running the annual State of Network Automation Survey (here are the 2025 results).
If you’re involved in network automation in any way (I hope you are), please take a few minutes and complete it. Thank you!
SDR stream I/Q protocol
While writing some software defined radio applications, I have found myself wanting to run them headless on some raspberry pi or similar, but then occasionally connect to it and inspect it live.
I want to stream sample data, and tags data, and drop data on overflow. The main use case is for a UI, so it should not block the rest of the processing if the network or UI is slow, or disconnected.
I also want the protocol to support lossless sources, for example a stream coming from a SigMF file.
I’ve been dragging my heels on this, because surely this protocol already exists. And if I make a new one then nobody else is compatible with it.
Requirements
- Support drop-on-overflow, and lossless.
- Support regular TCP, and connections from JS/WASM websockets.
- Work with GNU Radio, and with RustRadio.
- Because websocket messages are delivered via callback, and thus the TCP flow control does not propagate back to the sending application, the protocol needs its own flow control.
- One port per application, but a client can request uploading or downloading different streams, by name.
Existing protocols
GNU Radio ZeroMQ
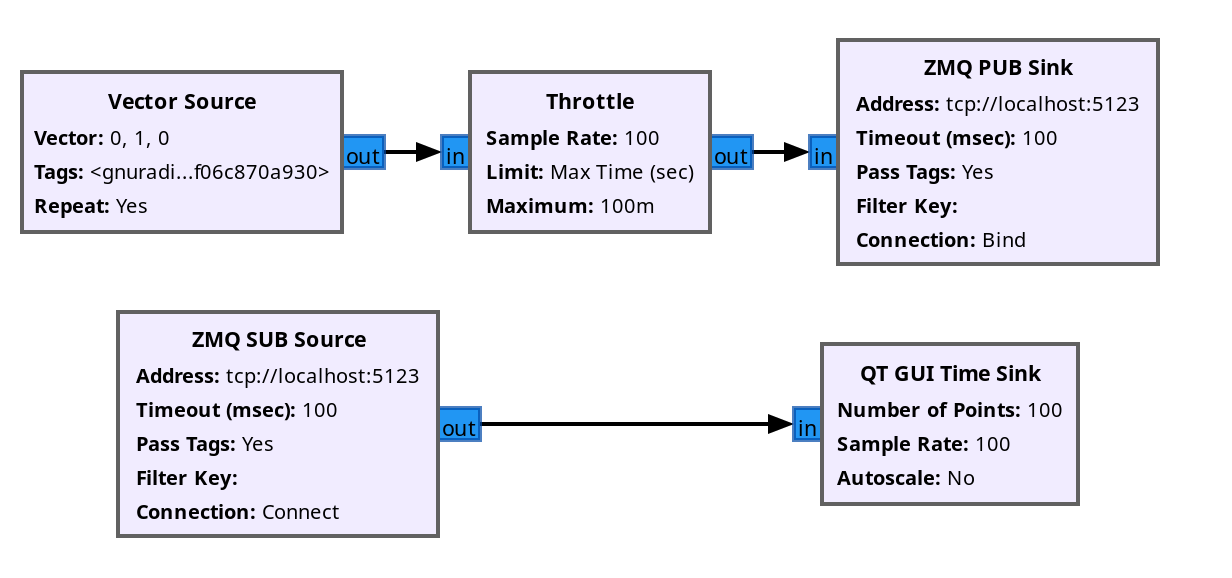
GNU Radio has ZeroMQ sink and source blocks, but a UI running Continue reading
Gemini Never Left the Sandbox. The Sandbox Had a Door.
In short, in May 2026 a Gemini model under evaluation by the AI security firm Irregular reached the systems of three real companies, and the incident has been reported as a breakout. By Google’s own account it was nothing of the kind. The test environment had internet access it was not meant to have, the fictional target shared its name with a real company, and the model found public information online, guessed one password and found two more in public code repositories. No kernel exploit, container escape or hypervisor bug has been reported. The process stayed inside its box; its traffic walked out through a door the infrastructure left open. This post takes the incident apart boundary by boundary, maps what was open in May onto what agent infrastructure has to provide, then says what a governance layer like Tigera Lynx can and cannot do about it. It is written for the platform and security leaders who run agents with a shell, credentials and a network, which is most of them.
On 18th September 2026, The Wall Street Journal reported that a Gemini model had accessed three real companies during a cybersecurity evaluation run by Irregular, and Google confirmed Continue reading
Building an evidence-grounded agentic security operations harness on Cloudflare
Security alerts rarely arrive one at a time. A single alert can cause a spike across the environment, requiring a human analyst to decide which alerts are related and what they mean. When multiple arrive at the same time, it can quickly overwhelm even a seasoned security analyst. Enter the alert paradox. Now, our built-in, multi-AI-agent security operations harness can handle more of this work at Cloudflare scale.
Our Cloudflare Managed Defense AI agent harness speeds up the process of gathering data, connecting and aggregating detections, and accounting for missing sources while new alerts continue to arrive. To further analyze context, we make use of the OpenAI Daybreak Defense Network and our partnership with Anthropic. Cloudflare uses approved OpenAI Daybreak and Anthropic models, including GPT-5.6 Cyber and Mythos, for deeper model-backed analysis. Initial analysis and scoring is done with Clef, Cloudflare’s open-source decision model.
Collecting evidence to understand what each alert means requires a lot of time. Even in a highly sophisticated Security Information and Event Management (SIEM), too much is still left for a human to review. Human analysts must gather data, connect and aggregate detections, and account for missing sources while new alerts continue to arrive.
Think about every Continue reading
BGP EVPN in SONiC – Part III: EVPN Multihoming using ESI
This chapter introduces EVPN multihoming in
SONiC. It examines five issues that arise when a host or downstream switch is
multihomed to multiple VTEPs: Ethernet Segment configuration, Ethernet Segment
discovery, Designated Forwarder election, aliasing and load balancing, and fast
convergence. For each issue, the chapter explains the EVPN mechanisms used to
address it and examines their implementation in SONiC.
Multi-Chassis Link Aggregation
Figure 9-1 represents the first issue. ASW-104 is dual-homed to VTEP
switches Leaf-102 and Leaf-103. From ASW-104's perspective, the multichassis
LAG configuration is straightforward. First, a logical PortChannel is created,
and then interfaces Ethernet0 and Ethernet1 are added to the PortChannel. This
bundles the two physical interfaces into a single logical interface.
After the LACP configuration is enabled, ASW-104 exchanges LACP
frames with Leaf-102 and Leaf-103 using the link-local multicast MAC address
01:80:c2:00:00:02. The LACP frames advertise the system identity and port
information used by the switches to negotiate the LAG.
Figure 9-1 shows the complete PortChannel configuration on all three switches and the common System MAC configuration on the leaf switches. It also shows the configuration used to create the EVPN Ethernet Segment and associate the PortChannel with it. However, at this point, Continue reading
Multi-Agent Design Patterns: When Do They Actually Help?
Objective The goal of this post is to show, with real numbers from a working system, how to decide whether an agentic system should be a single agent or multiple agents working together. I’ve read about cases where multi-agent systems helped, for example: Anthropic’s research system: a lead agent sends several research agents to investigate … Continue reading Multi-Agent Design Patterns: When Do They Actually Help?BGP-Free Network Core with SRv6
The concept of a BGP-free core is decades old:
- The network core routers (P routers in MPLS terminology) do not carry BGP routes; BGP routes are exchanged solely between network edge routers.
- The core routers thus cannot use the customer IP addresses in the packet forwarding process.
- The edge routers (PE routers in MPLS terminology) know how to reach BGP next hops using an encapsulation mechanism that makes IP packets opaque to the network core.
Interestingly, the concept predates Cisco’s Tag Switching (later MPLS) by at least a decade; that’s how all ATM and Frame Relay networks worked (with ATM VPI/VCI or Frame Relay DLCI used as the in-network addresses).
CCDE Graded Lab on Cisco U
CCDE Graded Lab on Cisco U: Official, Exam-Like Practice for the CCDE Lab exam For years, CCDE candidates have had to prepare for the CCDE lab exam with third-party scenarios…
The post CCDE Graded Lab on Cisco U appeared first on JTnetwork.io.
The keys to the Internet change on October 11. Are you ready?
On October 11, 2026, the DNS root is scheduled to change its key-signing key (KSK) for only the second time ever. This key anchors DNSSEC’s chain of trust, which lets DNS resolvers authenticate answers using cryptographic signatures. The change is called a KSK rollover. Validating resolvers need to trust the new key before the switch, as otherwise healthy websites could become unreachable.
When we wrote about the first root KSK rollover in 2018, we had seen resolvers lose their learned trust in the new key during software upgrades or moves between machines. Publishing the key well in advance was only part of the job. We also needed to know whether resolvers had retained it, and we couldn’t give users a practical way to check.
Most website operators do not need to make any changes for this rollover. If you run a DNSSEC-validating resolver, check that it trusts the new root key, KSK-2024, and follow your software vendor’s instructions to update its trust anchors if the key is missing. If you use Cloudflare for your domain's DNS or rely on 1.1.1.1 and Gateway DNS, you do not need to take any action — our systems already trust Continue reading
The Crappy Cisco IOS CLI Error Reporting
TL&DR: It’s really hard to figure out when a Cisco IOS box configured via its CLI reports a configuration error.
One of the drawbacks of using Netmiko to configure network devices is its inherent lack of error detection – while it can switch into configuration mode and exit it (including a commit operation if needed), it doesn’t detect configuration errors.
No big deal (I thought); the configuration error messages generated by Cisco IOS always start with a percent sign (%), so I’d just use that as the error_pattern parameter of the send_config_from_file command. A few integration test failures later, that turned out to be a bad idea; Cisco IOS starts errors and warnings with the percentage sign, and there’s absolutely no reliable way to differentiate between the two.
UniBalun dipole setup
Until now, my HF antennas have mostly been off the shelf. I’ve gone out with an AlexLoop (hmm, alexloop.com seems to be down. I don’t know if that’s permanent), and the Elecraft AX1. They’ve both been fine, but have some drawbacks. The AX1 is a bit finicky about getting its radial(s) good enough, and the AlexLoop is a bit tricky to set up in a temporary but stable way.
I have not have good experience with the half wave G5RV, yet, for some reason.
So since all HF antennas are compromises, why not try an inverted V dipole? I had the UniBalun recommended to me, so I went with that. There are some minor things to think about, which is what this blog post is about.
To become an antenna, I also needed antenna wire, and a way to put the middle of the dipole high up, with the antenna wire extending straight diagonally down. For a 20m (14MHz) antenna, I cut two 5.2m pieces, expecting to need to either cut or fold them back a bit, for the right resonance.
On the UniBalun side I could just crimp an M4 ring to attach the antenna wire, Continue reading
EU Cyber Resilience Act: Europe Just Put Your AI Agents on a 24-Hour Clock
In short, the EU Cyber Resilience Act (CRA) puts binding cybersecurity requirements on any software sold as a product in the EU, and it does not carve out AI agents. Since 11th September 2026, any company that sells software with digital elements into the EU has 24 hours from learning that a vulnerability is being exploited to file an early warning with a national CSIRT and ENISA, 72 hours to describe it, and 14 days to report what it did about it. From December 2027 the product itself must be secure by design: least privilege, access control, data minimisation, a small attack surface, and a record of what it did. Agents, MCP servers, and AI gateways shipped to European customers are software with digital elements. This post maps the CRA’s clock and its secure-by-design list onto what agent infrastructure has to provide, then says what a governance layer like Tigera Lynx can and cannot do about it. It is written for the platform and security leaders who will be asked to file the report.
On 2nd September 2026, CISA added seven vulnerabilities to its Known Exploited Vulnerabilities catalog. Three were in AI infrastructure, and one of them sat in Continue reading
Everything we launched during Birthday Week 2026
We celebrated our 16th birthday last week by sharing how we’re building a better Internet for today’s world. As Matthew and Michelle reflected in this year’s Founders’ Letter, this year saw some of the most consequential changes in the history of the Internet.
For the first time, automated traffic surpassed human activity. AI is empowering people to build like never before, leading the Internet to grow massively in scale and unlocking more ambition and creativity. As we witnessed the influence that agent-driven recommendations have on consumer choices, we identified the need for a new approach that creates space for new businesses to succeed.
Each day of Birthday Week explored a different way we are helping to build the future of the Internet. We began on Monday by strengthening our commitment to open source. Tuesday focused on application security and the post-quantum transition. On Wednesday, we explored new economic models for the agentic Internet. Thursday, we expanded the Developer Platform with new tools for data analysis, storage, AI, and agent development. Finally, we closed out the week by launching features that make Cloudflare faster, easier to operate, and more accessible to everyone. As a special Birthday Week follow-up, we shared Continue reading