Stuff The Internet Says On Scalability For August 2nd, 2019
Wake up! It's HighScalability time—once again:

Do you like this sort of Stuff? I'd greatly appreciate your support on Patreon. I wrote Explain the Cloud Like I'm 10 for people who need to understand the cloud. And who doesn't these days? On Amazon it has 52 mostly 5 star reviews (121 on Goodreads). They'll learn a lot and hold you in even greater awe.
Number Stuff:
Don't miss all that the Internet has to say on Scalability, click below and become eventually consistent with all scalability knowledge (which means this post has many more items to read so please keep on reading)...
Heavy Networking 463: Under The Hood Of 400G Ethernet With Cisco (Sponsored)
400G Ethernet switches will ship by the end of 2019. We get under the hood of the fastest-ever version of Ethernet to find out how it works, the challenges of building the gear, differences between QSFP-DD and OSFP optics, and more. Our guests are Ray Nering and Lane Wigley of Cisco, the sponsor for today's podcast.
The post Heavy Networking 463: Under The Hood Of 400G Ethernet With Cisco (Sponsored) appeared first on Packet Pushers.


Conference Packing – The Little Things
It seems like conference season never really ends. Between RSA, Cisco Live, Black Hat, and VMworld, I’m always running around to something. I enjoy being able to meet new people and talk to companies at these events but I also find that a little bit of planning ahead helps immensely.
There’s always a lot of discussion from people about what to pack for a conference. There have been some great posts written about it, like this one from Bob McCouch in 2014. He definitely covers all the important stuff that people would want to know, such as comfortable shoes and a bag big enough to carry extra things just in case you come back with enough fidget spinners to sink an aircraft carrier.
However, I’ve found in recent years that the difference between just surviving a conference and really being prepared involves a few extra items I never thought I’d need to bring back when I first started doing this in 2006. Maybe it’s the Scoutmaster in me, but being prepared has gone from being a suggestion to a necessity. And here are a few of those little necessities that I have found I can’t live without.
First? Aid.
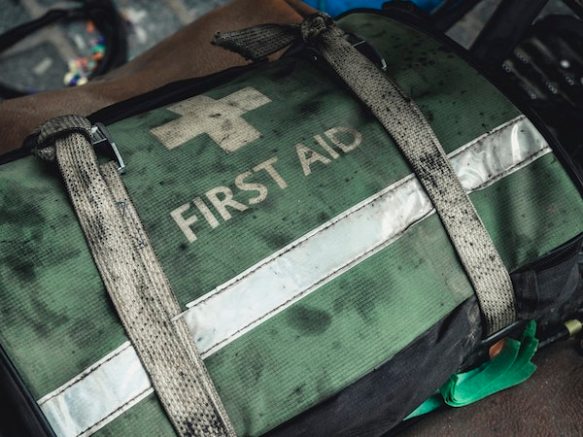
I’ve Continue reading
Connection Restored
I was embarrassed to realize recently that it’s been well over two years since my last blog post. Life has a way of getting away from you, I suppose. But I’ve decided to try and reboot the blog, and hopefully get back to writing regularly. Let me kick things off my sharing what I’ve been up to recently.
Goodbye, DigitalOcean!
After nearly five years working at DigitalOcean, I made the difficult decision to part ways with the company. In my time there, I was fortunate to work with an amazing team, and witness the truly amazing evolution of a startup company from niche player to major cloud provider. Most of all, I’m thankful to DigitalOcean for the opportunity my role provided in extending from traditional network engineering into development and automation. I’ll miss working with my DO team, but I’m excited to see where the future will take them.
Technology Short Take 117
Welcome to Technology Short Take #117! Here’s my latest gathering of links and articles from the around the World Wide Web (an “old school” reference for you right there). I’ve got a little bit of something for most everyone, except for the storage nerds (I’m leaving that to my friend J Metz this time around). Here’s hoping you find something useful!
Networking
- Ronald de Jong sheds some light on a potential “gotcha” with distributed multi-tier routing configuration in NSX. The key takeaway here is that anytime there is firewalling or other stateful services in place, the traffic will route to the (non-distributed) service router instead of just the distributed routers.
- Northbound Networks provides some information on the P4 programming language.
- Via the Packet Pushers blog, Daniel Himes provides a guide to a starting point for enterprise (network) automation.
Servers/Hardware
- AnandTech has a nice article on the future PCIe 6.0 spec, expected in to land in 2021.
Security
- Ronnie Flathers shares how he uses Docker for penetration testing.
- Interested in running Hashcat on AWS EC2? See this article by Ben Mason.
- Another data breach, this time from Capital One, hit the news this past week. Corey Quinn has his Continue reading
Securing BGP on the host with the RPKI
An increasingly popular design for a data-center network is BGP on the host: each host ships with a BGP daemon to advertise the IPs it handles and receives the routes to its fellow servers. Compared to a L2-based design, it is very scalable, resilient, cross-vendor and safe to operate.1 Take a look at “L3 routing to the hypervisor with BGP” for a usage example.

While routing on the host eliminates the security problems related to
Ethernet networks, a server may announce any IP prefix. In the above
picture, two of them are announcing 2001:db8:cc::/64. This could be
a legit use of anycast or a prefix hijack. BGP offers several
solutions to improve this aspect and one of them is to leverage the
features around the RPKI infrastructure.
Short introduction to the RPKI
On the Internet, BGP is mostly relying on trust. This contributes to various incidents due to operator errors, like the one that affected Cloudflare a few months ago, or to malicious attackers, like the hijack of Amazon Continue reading
Dynatrace Scores $544M IPO, Cloudflare to Follow Suit
Dynatrace raised $544 million in its initial public offering (IPO) today, selling 35.6 million...
Accessing the Docker Daemon via an SSH Bastion Host
Today I came across this article, which informed me that (as of the 18.09 release) you can use SSH to connect to a Docker daemon remotely. That’s handy! The article uses docker-machine (a useful but underrated tool, I think) to demonstrate, but the first question in my mind was this: can I do this through an SSH bastion host? Read on for the answer.
If you’re not familiar with the concept of an SSH bastion host, it is a (typically hardened) host through which you, as a user, would proxy your SSH connections to other hosts. For example, you may have a bunch of EC2 instances in an AWS VPC that do not have public IP addresses. (That’s reasonable.) You could use an SSH bastion host—which would require a public IP address—to enable SSH access to otherwise inaccessible hosts. I wrote a post about using SSH bastion hosts back in 2015; give that post a read for more details.
The syntax for connecting to a Docker daemon via SSH looks something like this:
docker -H ssh://user@host <command>
So, if you wanted to run docker container ls to list the containers running on a remote system, you’d Continue reading
BiB 081: 128 Technology Rethinks The WAN Router
128 Technology takes an interesting approach to WAN routing. In this Brief Briefing Ethan Banks and Drew Conry-Murray skim the surface of 128 Technology's approach, which includes stateful sessions, NAT, and encryption--but no tunneling. We also touch on use cases including SD-WAN and security. We also provide links to Networking Field Day videos that have much more detail.BiB 081: 128 Technology Rethinks The WAN Router
128 Technology takes an interesting approach to WAN routing. In this Brief Briefing Ethan Banks and Drew Conry-Murray skim the surface of 128 Technology's approach, which includes stateful sessions, NAT, and encryption--but no tunneling. We also touch on use cases including SD-WAN and security. We also provide links to Networking Field Day videos that have much more detail.
The post BiB 081: 128 Technology Rethinks The WAN Router appeared first on Packet Pushers.


Cisco Pays $8.6M in First-Ever Security Software Whistleblower Payout
It’s essentially pocket change for the vendor — Cisco CEO Chuck Robbin’s house sold for...
IBM Packs Red Hat OpenShift Into Cloud Paks
The Cloud Paks allow IBM software to run across major public cloud providers like Amazon Web...
Lanner and GTT Leverage uCPE to Bolster SD-WAN Performance
Both companies announced new SD-WAN capabilities leveraging universal customer premises...