D2DO312: Networking at Scale: AWS Transit Gateway War Stories
How can network architects successfully manage 95,000 hosts while navigating the complexities of large-scale cloud migrations? Devender Singh, a Principal Cloud Architect, joins Ned and Kyler to discuss the practical realities of managing network chaos, the migration from Transit Gateways to AWS Cloud WAN, and strategies for addressing the technical debt often encountered during enterprise... Read more »AI Agents on Kubernetes 101: From Laptop Script to Production Pod
In short, this is a beginner’s guide to deploying an AI agent on Kubernetes. You will containerize an agent, store its API key as a Kubernetes secret, write a deployment with health probes and resource limits, expose it with a service, and lock down its network egress, in that order, with a working manifest at every step. On a local kind cluster the whole walkthrough takes about an hour. At the end: the six mistakes almost every first agent deployment makes, and the questions a 101 deployment leaves open.
Every AI agent starts life the same way; a Python script on someone’s laptop, an API key in a .env file, a while loop around an LLM call. It works, it demos well. Then someone with a budget says “ship it,” and you, the engineer closest to the script, get to figure out what shipping an agent actually means.
This guide is that path, walked slowly. It assumes you know what a container is and have met kubectl at least once, and it assumes nothing about agents. By the end you will have an agent running in a cluster with its key in a Secret, its resource usage capped, its Continue reading
PP125: News Roundup—Cyberattack Impacts Pacemakers, OpenAI Publishes Eye-Opening Postmortem, and More
If it feels like everything is on fire, today’s News Roundup will not dispel that feeling. We discuss consumer routers that ship with factory-installed backdoors, US law enforcement agencies shutting down hacking domains, and how a threat actor tied to China is targeting Cisco IOS-XR routers. Android-based auto infotainment systems are susceptible to malware, OpenAI... Read more »HW087: Designing for 6GHz Standard Power Indoors
Keith welcomes David Coleman to examine the technical advantages and practical challenges of implementing standard power 6Ghz Wi-Fi in indoor environments. They also discuss automated frequency coordination (AFC), geolocation mechanisms for indoor APs, and LPI fallback strategy. AdSpot Sponsor: Meter Most IT teams are managing networks stitched together from years of acquisitions and vendor contracts... Read more »NB590: Blue Origin Wins NASA Bid for Mars Telecoms; Fortinet Offers High School Hackers Curriculum
Take a Network Break! We begin with follow-up on the Cisco/Teleport deal and Chinese models on US public clouds. Our Red Alert warns of two critical vulnerabilities in HPE’s Aruba Networking Fabric Composer, and we offer a quick heads-up on OpenAI and Anthropic outages and forthcoming security disclosures from Arista. On the news front, Broadcom... Read more »Testing Your Network with Netpicker
In my previous two posts, we covered what Pytest is, what it is traditionally used for, and how we can use it to test your network, checking things like BGP peer status, interface states, and so on. So far, we have looked at how to run these tests using the Pytest CLI command in the terminal.
In this post, we will look at Netpicker, a tool that takes the same Pytest tests and gives you a GUI to run and manage them, instead of relying on the command line.
What is Netpicker?
Netpicker is a tool that brings together config backups, security/compliance checks, and automation in one place. It supports 180+ network vendors, including Cisco, Juniper, Arista, Palo Alto, and Fortinet, and integrates well with tools like NetBox, Nautobot, and Infrahub for inventory, and Slurp'it for network discovery.
Under the hood, Netpicker uses pytest for its testing engine, but wraps it in a web GUI, so instead of running tests from the terminal, you run and manage them from a browser. This means you can run the same kind of pytest tests we covered in the previous two posts, things like checking BGP peer status or interface states, but Continue reading
Worth Reading: An Interactive Introduction to the STP
I can’t even start imagining how much time Vincent Bernat spent creating his interactive introduction to the spanning tree protocol (starting with STP implemented in WebAssembly); the results are simply phenomenal (there’s also a video version for people who forgot how to read).
I don’t think we’ll ever need another STP intro after this one ;)
Film Sci-Fi Tentang Hutan Bioelektrik dan Energi Petir Antariksa
Di tengah kemajuan teknologi dan perubahan iklim yang kian mendesak saat ini, konsep energi terbarukan menjadi bahan diskusi utama di berbagai sektor, termasuk dunia hiburan. Salah satu inovasi paling menarik yang sedang menjadi inspirasi dalam industri film adalah proyek pembangunan hutan bioelektrik—sebuah konsep futuristik yang menggabungkan bioteknologi dan energi alternatif untuk memanen energi dari fenomena petir antariksa. Artikel ini akan membahas bagaimana film sci-fi saat ini mengangkat tema hutan bioelektrik dalam narasinya, mengapa proyek ini begitu relevan untuk masa depan energi, serta dampaknya terhadap dunia hiburan dan kesadaran ekologis masyarakat.
Hutan Bioelektrik: Revolusi Energi Masa Depan dalam Film Sci-Fi
Konsep hutan bioelektrik merupakan ide revolusioner yang mengusung pembangunan menara mirip pohon sintetis yang mampu menyerap dan menyimpan energi dari petir antariksa. Dalam film-film sci-fi terkini, tema ini diangkat dengan latar dunia yang menghadapi krisis energi global akibat perubahan iklim ekstrem dan penipisan sumber daya fosil. Hutan bioelektrik dalam cerita fiksi ini digambarkan sebagai upaya terakhir umat manusia untuk mempertahankan kehidupan di Bumi sekaligus menjelajah ruang angkasa dengan sumber daya yang benar-benar berkelanjutan.
Film-film ini menampilkan lanskap sebuah ekosistem yang dipenuhi dengan menara menjulang tinggi yang tersusun dari material organik dan nano-elektronik, memungkinkan interaksi langsung dengan atmosfer planet dan badai Continue reading
Penelitian Indonesia Ungkap Sejarah Batu Penanda Tsunami Kerajaan Pesisir
Indonesia, dengan kekayaan sejarah dan geografi yang khas, semakin menonjolkan peranan pentingnya teknologi tradisional dalam mitigasi bencana. Salah satu temuan terkini yang menarik perhatian adalah penelitian mendalam mengenai batu penanda tsunami di wilayah pesisir Indonesia. Temuan ini bukan hanya menambah wawasan sejarah, tetapi juga mengangkat kembali teknologi kuno yang nyaris terlupakan dari era kerajaan-kerajaan pesisir yang pernah berdiri kokoh di Nusantara.
Pendahuluan: Pentingnya Batu Penanda Tsunami di Indonesia Saat Ini
Fenomena tsunami merupakan ancaman nyata bagi wilayah pesisir Indonesia. Seiring dengan frekuensi gempa bumi yang tinggi akibat posisi geografis negara ini di Ring of Fire, upaya mitigasi bencana berbasis sejarah dan kearifan lokal sangat diperlukan. Penelitian terbaru mengungkap keberadaan batu penanda tsunami yang digunakan oleh kerajaan-kerajaan pesisir masa lalu sebagai salah satu sistem peringatan dini. Batu penanda tsunami di Indonesia ini seolah menjadi saksi bisu sejarah serta perwujudan teknologi tradisional yang adaptif. Dalam konteks saat ini, pemahaman dan pelestarian teknologi ini bukan hanya bernilai sejarah, tetapi sangat relevan untuk pengembangan mitigasi bencana berkelanjutan.
Sejarah Batu Penanda Tsunami di Indonesia
Kerajaan-kerajaan pesisir di Indonesia, khususnya yang berkembang pada masa lalu di wilayah Sumatra, Jawa, dan Sulawesi, mempunyai tradisi kuat dalam mengelola risiko alam. Batu penanda tsunami menjadi salah satu inovasi sederhana Continue reading
Sidenotes with CSS anchor positioning
I am a heavy user of sidenotes:1 they keep optional content next to the text instead of sending the reader to the bottom of the page and back. Tufte CSS renders them without JavaScript but only accepts inline content. CSS anchor positioning, now supported by recent browsers,2 is an elegant alternative. Sidenotes can hold several blocks, still without JavaScript, and fall back below the paragraph referencing them on narrow viewports and older browsers.
In 2023, Eric Meyer demonstrated this technique in “Nuclear Anchored Sidenotes.” The main improvement over other solutions is that the notes can sit anywhere in the HTML document. You can place them after the paragraph referencing them, as regular block elements for text browsers, screen readers, feed readers, and reader mode to render them properly:

When the viewport is too narrow or the browser does not support CSS anchor positioning, you can style them so the reader can skip them or glance at them without losing their position in the text:

Once the viewport is large enough, they appear in the margin, at the same vertical position as the Continue reading
SONiC Deep Dive: BGP Update Message Processing
BGP Route Advertisement
The next step after configuring BGP
peering using BGP Unnumbered with IPv6 link-local addresses is to advertise the
host networks. The lower part of Figure 6-10 shows the sonic-cli configuration
commands used to advertise the local VLAN subnet on each leaf. On Leaf-101, we
advertise 10.0.10.0/24, which is the subnet for VLAN 10. On Leaf-102, we
advertise 10.0.20.0/24, which is the subnet for VLAN 20.
By examining the BGP Loc-RIB on
Leaf-102, for example, we can see that the next hop for 10.0.10.0/24,
originated on Leaf-101, is the IPv6 link-local address of Spine-11's Ethernet0
interface.

Figure 6-10:
IPv4 Routes Installed in the BGP Loc-RIB Table.
Figure 6-11 verifies that the host
subnets learned through BGP have been installed in the IP routing table on all
switches. For example, the destination prefix 10.0.10.0/24 is installed on
Leaf-102 with the next hop fe80::e22:34ff:feb6:a and the outgoing interface
Ethernet0.
This also illustrates the separation between the BGP control plane and the data plane. BGP uses IPv6 link-local addresses to establish the BGP session and exchange BGP messages carrying IPv4 NLRI, with an IPv6 link-local address specified as Continue reading
TNO071: The Network Team Is Drowning. Is AI the Life Raft? (Sponsored)
Last year, 49,000 CVEs were published, more than 130 new vulnerabilities every day. So what actually happens with all of those CVEs in your network infrastructure? In this sponsored episode, Rekha Shenoy and Irfahn Khimji of BackBox join Scott Robohn to discuss why the math of manual network operations no longer works, where traditional tools... Read more »HN840: How to Make a Technology Buying Decision
When engineers look to buy new technology they tend to focus on features and functionality, but there’s more to it than that. Sian Morgan joins Drew and Ethan to discuss the best practices involved in making a good technology buying decision. Sian shares how engineers can align their technical focus with broader business objectives, calculate... Read more »Please Help Me Follow Your Content
Finding good content in the swamp of AI slop is hard, and whenever I find a blog post worth reading, I’d like to know when the author publishes the next one.
For stupid reasons (like a day having only 24 hours, and me having a life), I can’t periodically scan all websites I find interesting, but fortunately, I don’t have to. Two well-known mechanisms work reliably: email updates and RSS feeds.
Meet Mylo: An AI-native way to work with Calico
A library of Calico tools and skills — delivered through the Calico MCP Server
What if your hardest network question took ten minutes instead of ten days?
Anyone who has operated Kubernetes networking at scale knows the shape of a bad day. A request that should succeed is quietly failing. The application team swears nothing changed. Somewhere across a stack of tiers, selectors, and policies, some written last week and some inherited from an engineer who left two years ago, a rule is denying the traffic. Finding it means reading YAML, cross-referencing flow logs, and reconstructing the policy evaluation order in your head. For a genuinely knotty case, that work can stretch across days and pull in more than one team before anyone gets to the bottom of it.
I think that day is about to get a lot shorter. Today we’re introducing Mylo, an expert for Calico that works inside the AI tools your teams already use. Ask Mylo why a pod can’t reach a service, and it traces the path, points to the exact policy and rule doing the blocking, and explains why in plain language, in about the time it took you to read this paragraph. Mylo Continue reading
IPB207: Flying Blind: Monitoring Might Not See IPv6
Is your current network monitoring infrastructure capable of seeing IPv6 traffic or are you flying blind in a dual-stack environment? Today Ed, Nick, and Tom explore the critical challenges surrounding IPv6 visibility such as the limitations of vendor tools and the complexities of maintaining observability as networks evolve.N4N063: Link Layer Discovery Protocol
Ethan and Holly tackle the Link Layer Discovery Protocol (LLDP). They explain how this protocol helps network engineers map network topologies and validate wiring. They also discuss how LLDP devices use frames to send information, mandatory and optional type length values (TLVs), and why security on edge ports remains critical. Episode Links: Watch this episode... Read more »BGP-Free Core with SR-MPLS
The beauty of SR-MPLS is that it’s a drop-in replacement for the traditional (LDP- or RSVP-based) MPLS control plane. For example, you could replace LDP with SR-MPLS in a network using MPLS to implement a BGP-free transport core, and it just keeps working.
This scenario was the first “fun” scenario in the ITNOG10 Segment Routing workshop. The core network uses the same topology as in the previous examples; I added two hosts and BGP routing.
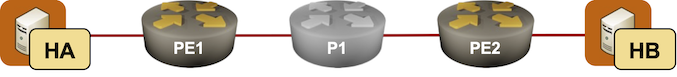
Simplest possible network using a BGP-free core