BIB096 Considering KPIs For Network Operations
I was asked what Key Performance Indicators would I consider for an operational data network. I spent an hour coming up with ideas and here they are.BIB096 Considering KPIs For Network Operations
I was asked what Key Performance Indicators would I consider for an operational data network. I spent an hour coming up with ideas and here they are.
The post BIB096 Considering KPIs For Network Operations appeared first on Packet Pushers.
The Hedge Podcast Episode 42: Andrei Robachevsky and MANRS
The security of the global routing table is foundational to the security of the overall Internet as an ecosystem—if routing cannot be trusted, then everything that relies on routing is suspect, as well. Mutually Agreed Norms for Routing Security (MANRS) is a project of the Internet Society designed to draw network operators of all kinds into thinking about, and doing something about, the security of the global routing table by using common-sense filtering and observation. Andrei Robachevsky joins Russ White and Tom Ammon to talk about MANRS.
Working with TC on Linux systems
Hi folks! Long time no talk : ) Life has been incredibly busy for me over the last few months so I’ll apologize in advance for the lack of posts. However – I’m aiming to get back on the horse so please stay tuned!
With that out of the way – I wanted to spend some time in this post talking about the command line tool found on Linux systems called tc. We’ve talked about tc before when we discussed creating some network/traffic simulated topologies and it worked awesome for that use case. If you recall from that earlier post tc is short for Traffic Control and allows users to configure qdiscs. A qdisc is short for Queuing Discipline. I like to think of it as manipulating the Linux kernels packet scheduler.
Note: tc is traditionally part of the iproute2 toolset which Im pretty sure (but not positive) is included in most base Linux distros these days.
When tc comes up – it’s easy to immediately start thinking about QOS, queuing, and packet(traffic) control. And while some of the actions available to you when using tc seem obvious, or at least fit within the mindset of queue disciplines (the drop Continue reading
Open Standards Everywhere: How the Kolkata Chapter Got a Perfect Score

In early May 2020, the Open Standards Everywhere (OSE) project held a series of virtual training sessions for Internet Society Chapters. Over 70 Chapter representatives from around the world learned, in English, French, or Spanish, how to improve the overall security and availability of their Chapter’s websites and web servers by enabling IPv6, HTTP/2, TLS, and DNSSEC.
To assess everyone’s progress we tested each Chapter’s website before and after the training sessions using internet.nl and http2.pro. As a result of the OSE training sessions, many Chapters were able to significantly increase their website’s compliance. But one Chapter in particular, ISOC Kolkata, was able to take its website from 32% compliance to a whopping 100%. We caught up with ISOC Kolkata member Rittika Ratawa, who was nominated by the Chapter to attend the training, to find out more.
The Internet Society: What changes did you make to isockolkata.in as a direct result of the OSE virtual training session?
Rittika: After the training session, the Chapter made several changes. Firstly, we changed our DNS service provider as the one we had been using did not offer DNSSEC services or IPv6. Then we enabled DNSSEC by providing Continue reading
Urban Terror Server on Cisco CSR1000v
We have discussed the configuration of Guest Shell on Cisco CSR 1000v platform in a previous tutorial. The guest shell is a built-in Linux container with CentOS 7 installed, which can be activated on the fly when Linux applications are needed. Our lives are currently affected by SARS-CoV-2 and long-standing quarantine, so why not do […]Continue reading...
DevAsc – Python Script To Collect Show Commands Output
A colleague needed to connect to several Cisco devices, run some show commands, and save the output. I decided it would be good to practice my Python skills so I coded something together.
Why didn’t do you do this in Ansible, Nornir, or other tool of choice? Because the goal was to learn Python, not minimize amount of work to solve the task.
This work was highly inspired by others such as Debi, John, and wouldn’t be possible without the work from Kirk. Also thanks to Patrick, and Nick for giving me pointers on the code.
From a high level, the script will perform the following tasks:
- Read commands from a text file “commands.txt”
- Read devices from a text file “devices.txt”
- Ask the user for credentials
- Log in to the devices
- Perform show commands
- Save the output to a text file per device
In order to perform the tasks, the script relies on several modules:
Colorama – Used to color code terminal output
Netmiko – Used to setup SSH connection to device and parse the output
Datetime – Used to create a timestamp
Getpass – To get password from user without displaying it to the Continue reading
Wave Glider Robots

This video opened my mind to the ideas of robotic surveillance and data capture of the ocean. Wide range of civilian applications of course. But also police applications for customs and policing for monitoring the seaways around a country. And the military applications for defense and detection. Potentially even delivering a torpedo style payload.
The post Wave Glider Robots appeared first on EtherealMind.
Deep dive on Cisco ASA resource modules
Recently, we published our thoughts on resource modules applied to the use cases targeted by the Ansible security automation initiative. The principle is well known from the network automation space and we follow the established path. While the last blog post covered a few basic examples, we’d like to show more detailed use cases and how those can be solved with resource modules.
This blog post goes in depth into the new Cisco ASA Content Collection, which was already introduced in the previous article. We will walk through several examples and describe the use cases and how we envision the Collection being used in real world scenarios.
The Cisco ASA Certified Content Collection: what is it about?
The Cisco ASA Content Collection provides means to automate the Cisco Adaptive Security Appliance family of security devices - short Cisco ASA, hence the name. With a focus on firewall and network security they are well known in the market.
The aim of the Collection is to integrate the Cisco ASA devices into automated security workflows. For this, the Collection provides modules to automate generic commands and config interaction with the devices as well as resource oriented automation of access control lists Continue reading
Making the WAF 40% faster
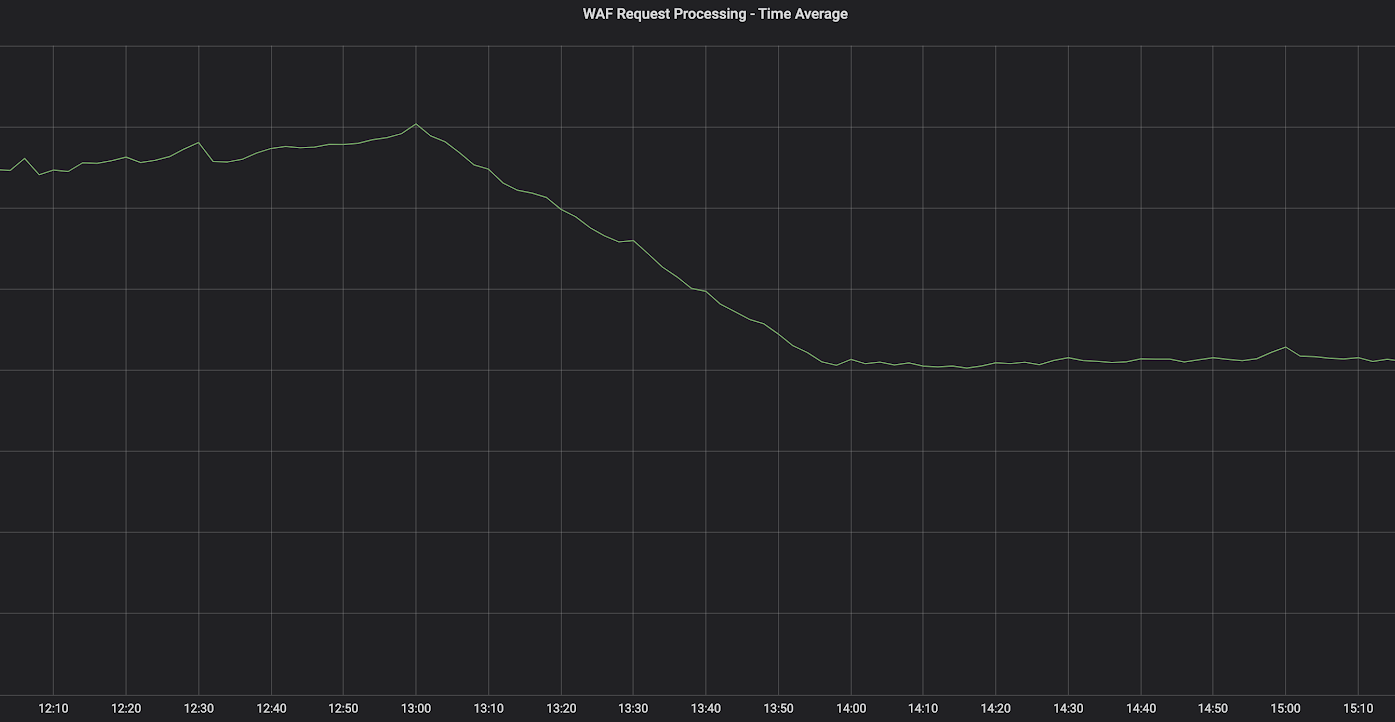
Cloudflare’s Web Application Firewall (WAF) protects against malicious attacks aiming to exploit vulnerabilities in web applications. It is continuously updated to provide comprehensive coverage against the most recent threats while ensuring a low false positive rate.
As with all Cloudflare security products, the WAF is designed to not sacrifice performance for security, but there is always room for improvement.
This blog post provides a brief overview of the latest performance improvements that were rolled out to our customers.
Transitioning from PCRE to RE2
Back in July of 2019, the WAF transitioned from using a regular expression engine based on PCRE to one inspired by RE2, which is based around using a deterministic finite automaton (DFA) instead of backtracking algorithms. This change came as a result of an outage where an update added a regular expression which backtracked enormously on certain HTTP requests, resulting in exponential execution time.
After the migration was finished, we saw no measurable difference in CPU consumption at the edge, but noticed execution time outliers in the 95th and 99th percentiles decreased, something we expected given RE2's guarantees of a linear time execution with the size of the input.
Day Two Cloud 055: Securing Cloud Infrastructure And Applications
Security is difficult and tricky, but we've got an amazing guest on today's Day Two Cloud podcast to help you improve your security posture and manage your cloud risk. Our guest is Tanya Janca, Founder, Security Trainer, and Coach at She Hacks Purple. We discuss key security areas including the network, identity, and applications; taking advantage of cloud visibility; securing SaaS apps; and more.Day Two Cloud 055: Securing Cloud Infrastructure And Applications
Security is difficult and tricky, but we've got an amazing guest on today's Day Two Cloud podcast to help you improve your security posture and manage your cloud risk. Our guest is Tanya Janca, Founder, Security Trainer, and Coach at She Hacks Purple. We discuss key security areas including the network, identity, and applications; taking advantage of cloud visibility; securing SaaS apps; and more.
The post Day Two Cloud 055: Securing Cloud Infrastructure And Applications appeared first on Packet Pushers.
Create a Windows 10 bootable USB on MacOS
How to create a windows 10 bootable USB from MacOS.What is Edge Computing? Here’s Why It’s Important
Edge Computing seems to be a hot topic these days but what does it really mean and why is it...Modular networking in a volatile business environment
Organizational change, growth, and environmental diversity are all challenges for IT teams, and they’re going to be a part of everyday life for the foreseeable future. As the number of device models and network architectures increases, so, too, does management complexity. Coping with 2020’s ongoing gift of unpredictability requires technological agility, something Cumulus Networks, acquired by NVIDIA, can help you with.
It’s easy to worry about the consequences of our collective, rapidly changing economic circumstances as though the problems presented are somehow novel. They’re not.
2020 has increased uncertainty, leading to an increased velocity of change, but change is the only constant in life, and the need for agile networking has been obvious to many in the industry for some time. Even without problems like having to rapidly figure out how to cope with large chunks of the workforce working from home, change-responsive networking has been a challenge for organizations experiencing growth for decades, a problem many continue to struggle with today.
At a practical level, one of the biggest problems with rapid change is that it quickly leads to a dilemma: precisely meet the needs of the moment, resulting in a significant uptick in equipment diversity, or deploy Continue reading
Big Blue Open Sources The Core Inside BlueGene/Q Supercomputers
Earlier this month, we were talking to the James Kulina, the new executive director of the OpenPower Foundation, which is the organization created by IBM and Google back in the summer of 2013 to create a community around the Power architecture. …
Big Blue Open Sources The Core Inside BlueGene/Q Supercomputers was written by Timothy Prickett Morgan at The Next Platform.
Simplifying secrets management with CyberArk and Red Hat Ansible Automation Platform
Access credentials and secrets are a crucial piece of today’s infrastructure management: if they get compromised, the environment itself is at risk. Thus some time ago, back at about version 3.5.1, the idea of a secrets management system was introduced into Ansible Tower, one of the components of our Red Hat Ansible Automation Platform. What this essentially means is that Ansible Tower has a credential store where it will encrypt at-rest secrets that you need in order to log in to a remote host, authenticate with a cloud endpoint or pull content from a version control system.
We have always needed secrets in order to log in and then configure a remote resource. We do this every day with usernames and passwords. Ansible Tower has a very secure built-in mechanism for providing this capability, but some may see that as an additional security island or bespoke to the enterprise direction. In this blog post, I will highlight the Ansible way of solving the “security island” problem and propose a solution using Ansible credential plugins integration via CyberArk Conjur. Conjur is an API addressable vault where you store access and authorization information instead of having the secrets stored Continue reading
Heavy Networking 526: Rethinking Your Global Enterprise WAN With Telia Carrier (Sponsored)
In today’s sponsored Heavy Networking podcast we talk to Telia Carrier. Telia runs its own global IP backbone, and as the public Internet becomes the de facto enterprise WAN, your choice of carrier becomes critical. Our guest is Mattias Fridström, Vice President & Chief Evangelist at Telia Carrier. We discuss why enterprises should consider Telia services including DCI, cloud connections, and SD-WAN.Heavy Networking 526: Rethinking Your Global Enterprise WAN With Telia Carrier (Sponsored)
In today’s sponsored Heavy Networking podcast we talk to Telia Carrier. Telia runs its own global IP backbone, and as the public Internet becomes the de facto enterprise WAN, your choice of carrier becomes critical. Our guest is Mattias Fridström, Vice President & Chief Evangelist at Telia Carrier. We discuss why enterprises should consider Telia services including DCI, cloud connections, and SD-WAN.
The post Heavy Networking 526: Rethinking Your Global Enterprise WAN With Telia Carrier (Sponsored) appeared first on Packet Pushers.