A revisit of remote Spectre attacks on Cloudflare Workers

In 2021, we assessed remote Spectre attacks against Cloudflare Workers. Based on the results, we shipped a production defense called Dynamic Process Isolation (DyPrIs), which identifies maliciously looking scripts and isolates them into separate processes. Since then, newer techniques in the area of stabilizing Spectre attacks have been discovered. To understand if these techniques posed a threat to our Workers production environment, we decided to internally reassess the remote Spectre attack. Building an updated proof-of-concept on the production environment allowed us to empirically assess the risk of Spectre attacks under production workloads. 

To mount a successful side-channel attack in production, an external attacker has to overcome additional obstacles such as activity on shared hardware resources, interrupts, context switches, and coarse-grained timers. Our research uncovered a limitation in the implementation of DyPrIs and we managed to demonstrate a remote Spectre attack reliably leaking up to 12 bit/s with a 99% accuracy in the production environment of Cloudflare Workers. As a consequence of this research, we improved DyPrIs, integrated the V8 Sandbox and an in-process isolation mechanism to further reduce the risk of memory disclosure attacks. 

Today we are publishing a paper describing our findings, co-authored by Albert Pedersen, Haocheng Continue reading
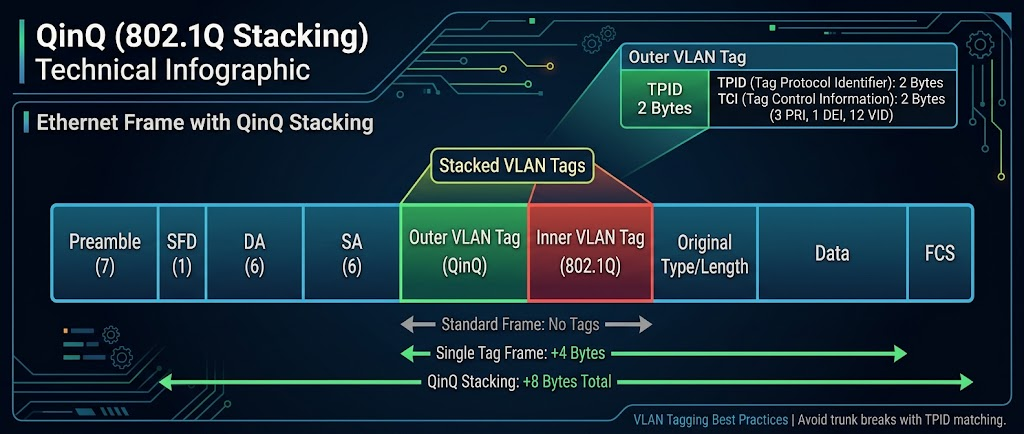
New Tool – VLAN / QinQ Tag Overhead Calculator

New on the Network Tools page: a VLAN / QinQ Tag Overhead Calculator. It exists because of the same problem that led to the MTU / Encapsulation Overhead Calculator — vendors don’t agree on what a config knob actually means, and it costs you an afternoon before you find that out.

The history behind this one

The MTU tool exists because mtu isn’t the same number on every platform. Classic Cisco IOS treats it as the L3 payload size. Junos and IOS-XR fold the 14-byte Ethernet header into it. Same command, same-looking number, two different frames on the wire — and the failure mode is never an error message, it’s just silent fragmentation or a black-holed jumbo-frame flow that only shows up under load.

Worth Reading: On AI Coding and Its Discontents

A lot of AI-coding enthusiasts are making claims along the lines of “AI coding tools are like compilers; you supply intent, they translate it into code, and who ever looked at the machine-code output?” Unfortunately, there is a bit of a gap between hope and reality; traditional compilers were always deterministic, and are (after decades of development and bug-fixing) pretty much bug-free. AI coding tools are neither, and no amount of “agentic loops” will solve that.

BGP Role model: tracking the adoption of RFC 9234

Route leaks push traffic down paths it was never meant to take. We have written and spoken publicly in the past about route leaks in Border Gateway Protocol (BGP), depicting these events as impactful incidents that cause misdirection of traffic through unintended network paths. BGP routing is driven by the relationships between Autonomous Systems (ASes), i.e., customer-provider and peer-peer. Customers pay providers for access to the rest of the Internet, while peers exchange traffic with one another typically under a “settlement-free” arrangement where no money changes hands. These relationships help define routing rules that form plausible paths. For example, the rules form a “valley-free” hierarchy of how routes should propagate: a route learned from a provider or a peer should be announced only downward to customers, never back up to another provider or peer. Rules like this express an intent or expectation about Internet routes. A route leak is what happens when that intent is violated.

Historically, each network has had to implement this intent on its own, using complex, error-prone routing policies. RFC 9234 (Route Leak Prevention and Detection Using Roles in UPDATE and OPEN Messages) simplifies this by expressing intent within the protocol Continue reading

Exploring the BGP Neighbor CONNECT State

Sakar left an interesting comment on my The Curious Case of the BGP Connect State blog post, claiming that Cisco IOS/XE goes through a CONNECT state when opening an incoming BGP session.

I wanted to double-check this behavior, so I needed a scenario where one router would keep sending TCP SYN requests, the other would not (or we wouldn’t learn anything), and the two routers could not communicate (or they’d quickly go into the OPEN state).

Here’s my first attempt at meeting those requirements:

Broadband RF scanner revisited

I have previously blogged about doing RF surveys using software defined radio. The most interesting aspect to me has been to inventory the business of the different WiFi channels, in order to not clash with neighbouring access points.

I’ve now written better software for doing these surveys.

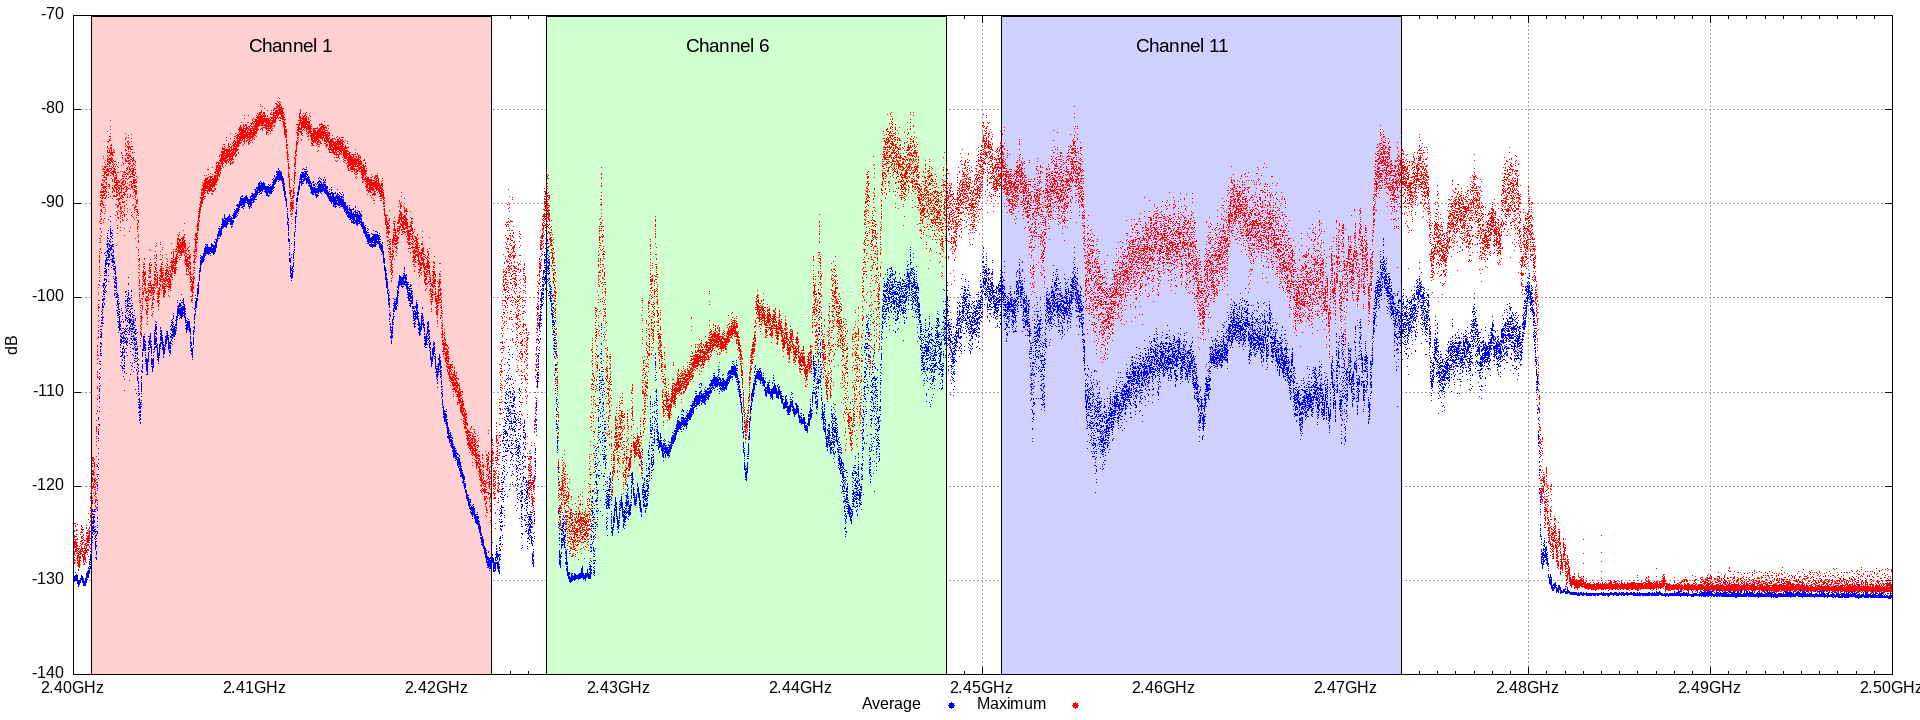
2.4GHz is a mess (overlapping channels), has much less spectrum, and goes through walls more than 5GHz worth. There’s also a bunch of other crap on 2.4GHz polluting the airwaves, including microwave ovens. So if you’ve thought about this at all, you know to stay off of 2.4GHz.

It’s tempting to get a QuadRF in order to add more dimensions to the 5GHz RF survey, but so far I’ve resisted buying this particular toy.

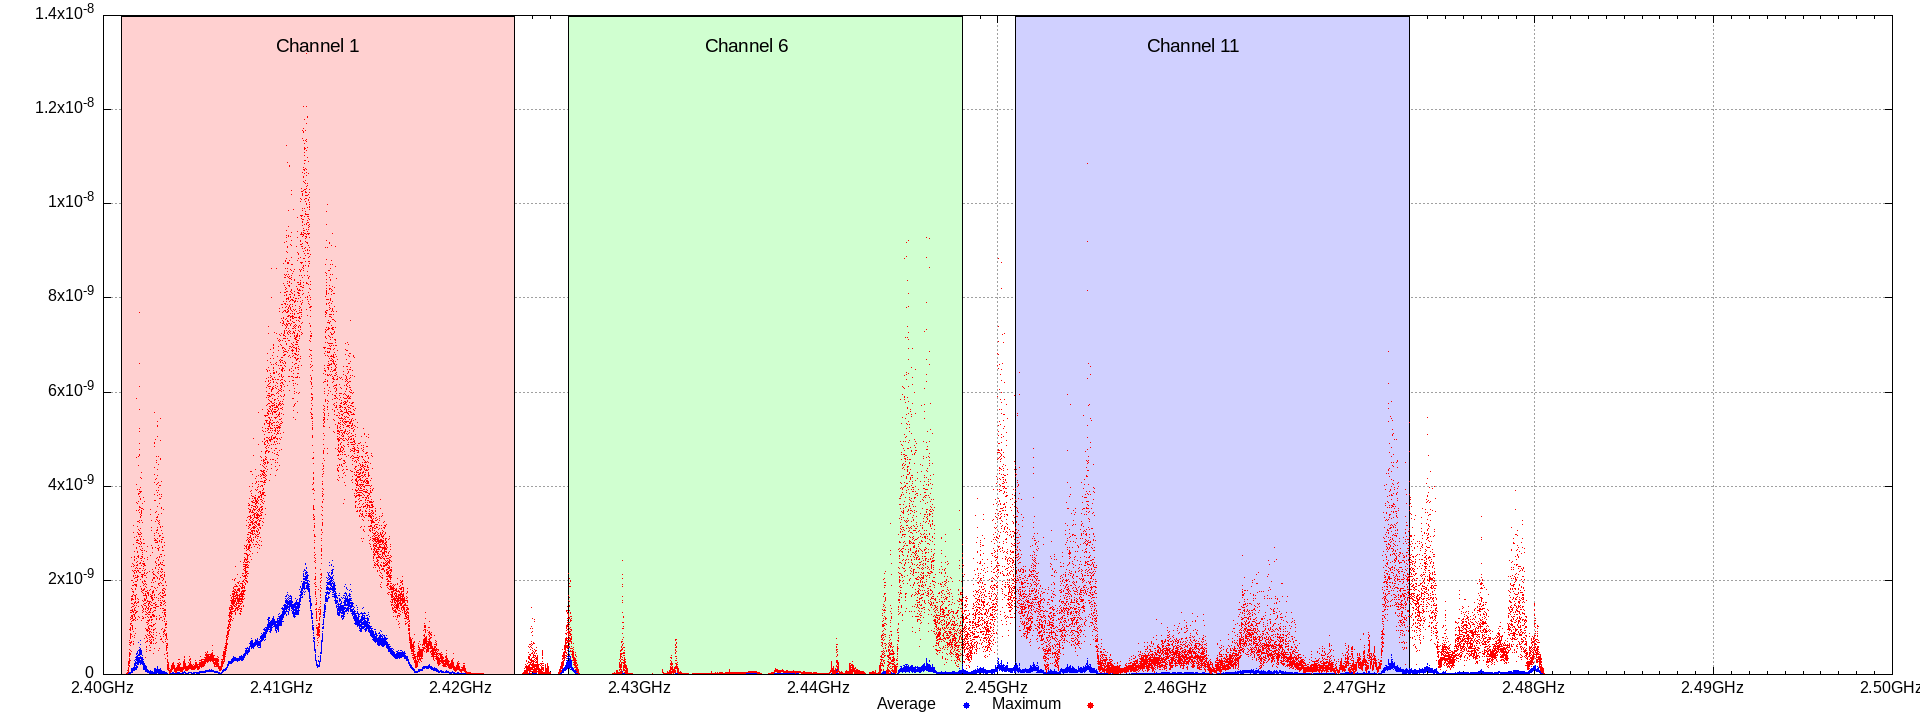
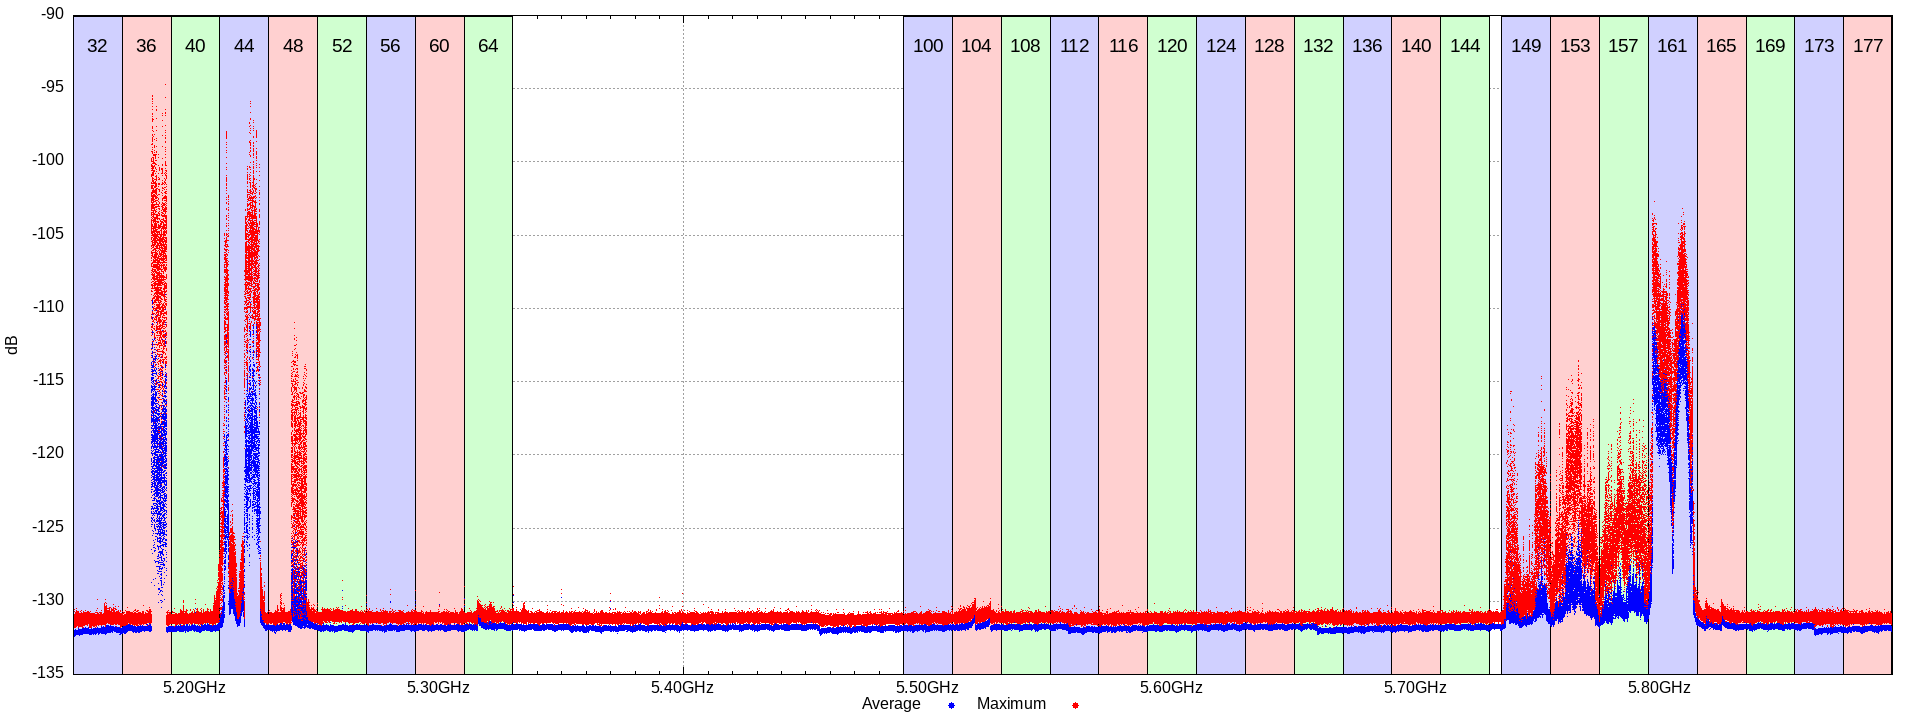
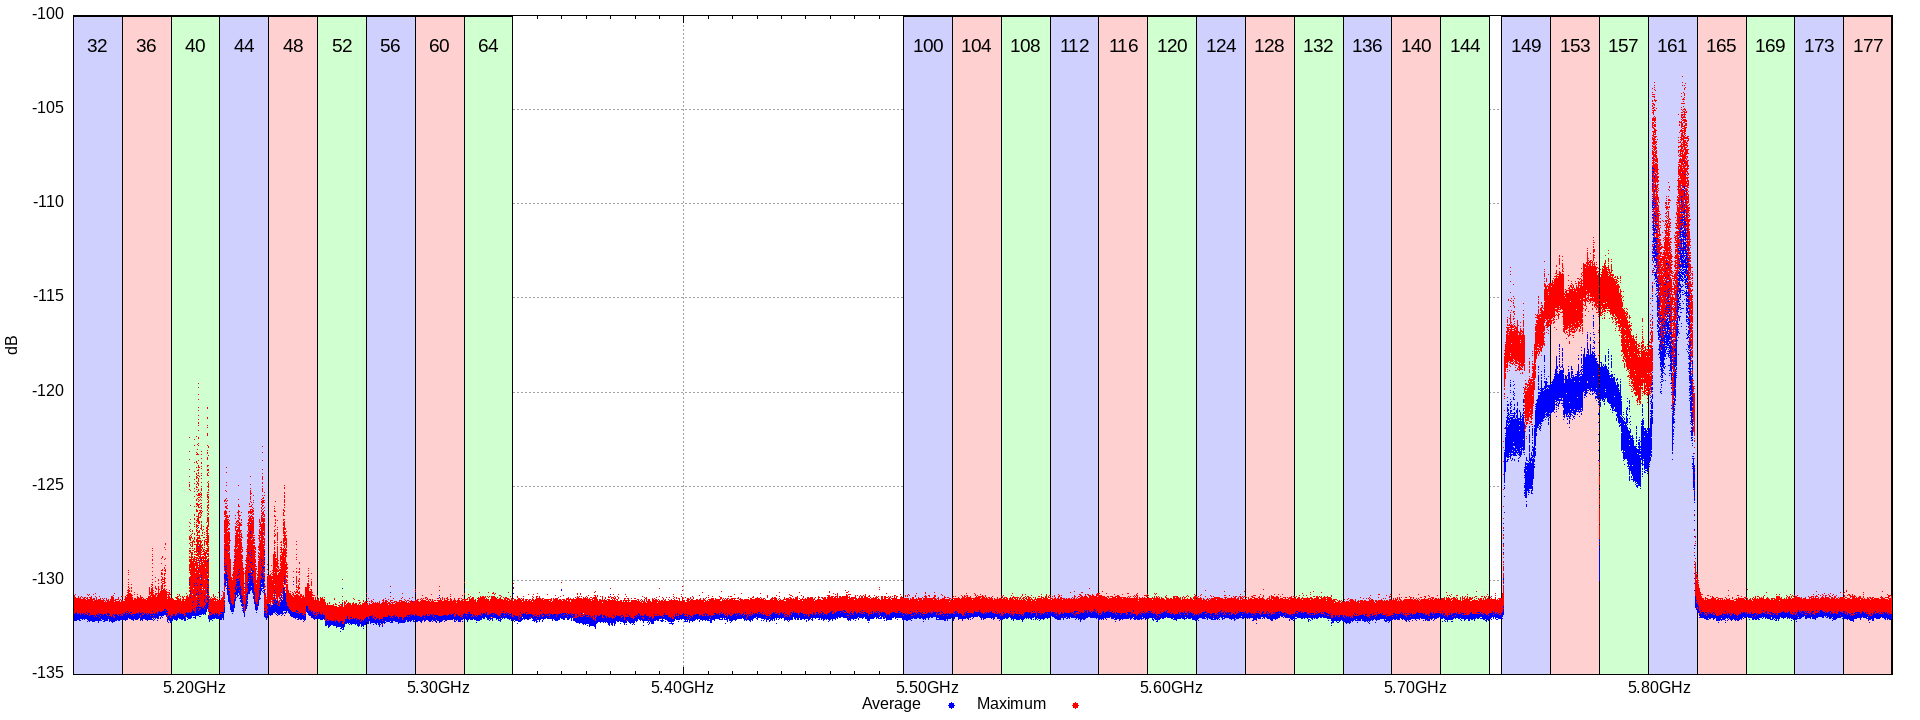
I’m plotting the spectrum power in both dB and linear. With linear scale the busyness really pops.

2.4GHz

As expected, this is a mess: 2.4GHz dB 2.4GHz linear

There’s even a bunch of noise between the channels. Is it microwaves? Or someone running the 1/5/9/13 channel split? No, if anything it looks like channel 14, which is not legal here.

5GHz

Background traffic

5GHz dB 5GHz linear

Busy

5GHz dB, busy 5GHz linear, busy

As a power WiFi user I started using U-NII-3 channels (149-165) as soon as they Continue reading

SONiC Deep Dive: Intra-Switch Inter-VLAN Routing and Packet Forwarding


The title of this section might seem a little overwhelming, but it reflects the focus of the chapter. The SONiC Redis database programming pipeline is examined through the configuration of two Layer-2 VLANs, VLAN 10 and VLAN 20, together with their respective Layer-3 routing interfaces.

VLAN 10 and VLAN 20 represent two separate Layer-2 broadcast domains, with each VLAN associated with its own IP subnet. VLAN 10 uses the 10.0.10.0/24 subnet, while VLAN 20 uses the 10.0.20.0/24 subnet. Because the two hosts belong to different broadcast domains and IP subnets, communication between them requires Layer-3 routing. In this example, the routing is performed locally by Leaf-1 through the routing interfaces configured for the two VLANs.

Figure 5-15 depicts the basic building blocks and IP addressing scheme used in this example. PC1, with IP address 10.0.10.101/24, belongs to VLAN 10 and is connected to the Leaf-1 Ethernet0 interface. PC2, with IP address 10.0.20.101/24, belongs to VLAN 20 and is connected to the Leaf-1 Ethernet1 interface. The routing interfaces for VLAN 10 and VLAN 20 use IP addresses 10.0.10.1/24 and 10.0.20.1/24, respectively.

The Continue reading

New Tool – Juniper Protect-RE Filter Generator

Also new on the Network Tools page: a Juniper Protect-RE Filter Generator — builds the lo0.0 input firewall filter every RE-bound packet passes through, regardless of which interface or destination address it actually arrived on.

Check the protocols you run, list trusted sources where it matters, and get a complete, correctly-ordered config — anti-spoofing and fragment discard first, then source-restricted NTP/RADIUS/SNMP/BGP, then OSPF/VRRP, then management access, a blanket TCP SYN/FIN/RST flood policer, type-restricted rate-limited ICMP, dual-style traceroute support (UDP and Windows’ ICMP-based tracert), optional BFD, and a logged, counted catch-all discard at the end.

The Never-Ending IPv6 Loopback Prefix Saga

Remember the sage advice to simplify your life and use the IPv6 /64 prefixes everywhere? Not only does it make your life simpler (and wastes immesuarably less address space than the crazy “let’s assign /64 to every device” stupidity), it also reduces the hardware requirements in your high-speed routers layer-3 switches. You see, doing lookups on 64 bits uses half the silicon it takes to do lookups on 128 bits.

Alas, some people never got the memo. OSPFv3 standard clearly states in one of the bullets in section 4.4.3.9 that the loopback prefixes should always be advertised as /128s regardless of what’s configured on the interface.

SONiC Deep Dive: Binding Interface to Vlan

Step 3: Associate Ethernet0 to VLAN 10

After configuring VLAN 10 and bringing up interface Ethernet0, the next step is to make Ethernet0 an untagged member of VLAN 10.

GONFIG_DB and APPL_DB

Figure 5-11 gives a conceptual view of the Redis database updates resulting from the SONiC command:

sudo config vlan member add 10 Ethernet0 --untagged

The command defines our intent: Ethernet0 should participate in VLAN 10 as an untagged (access) port. For an untagged VLAN member, frames received from the host arrive without an 802.1Q tag and are associated with VLAN 10 based on the port's VLAN membership. In the opposite direction, frames transmitted from VLAN 10 toward Ethernet0 are sent without an 802.1Q tag.

The command updates several related entries in CONFIG_DB. The PORT|Ethernet0 entry contains the port's access VLAN configuration:

PORT|Ethernet0

    access_vlan = 10


The VLAN|Vlan10 entry represents the VLAN itself and contains a members@ field that records Ethernet0 as a member:


VLAN|Vlan10

   members@ = Ethernet0   

   vlanid = 10


The @ character in members@ is part of the SONiC CONFIG_DB schema convention. The members@ value is a configuration representation of the relationship between the VLAN and its members.

The Continue reading

Misteri Fenomena Crystal Reinforcement Lattice pada Ice Shelf

Fenomena crystal reinforcement lattice pada dasar lapisan es di kutub menjadi salah satu topik yang paling mencuri perhatian dalam penelitian perubahan iklim dan dinamika es saat ini. Struktur kristal unik ini ditemukan di bawah lapisan es laut, yang berperan penting dalam mempertahankan stabilitas dan kekuatan lapisan es tersebut. Pada periode terbaru, pemahaman mengenai crystal reinforcement lattice semakin berkembang, membuka wacana baru tentang bagaimana interaksi kimia dan fisika pada tingkat mikro dapat memengaruhi ketahanan dan masa depan es kutub di tengah krisis iklim global.

Apa Itu Crystal Reinforcement Lattice pada Ice Shelf?

Secara sederhana, crystal reinforcement lattice adalah struktur kristal yang terbentuk secara alami di bawah lapisan es laut, khususnya pada bagian basal ice shelf, yakni di perbatasan antara es dan laut cair. Struktur ini berfungsi sebagai sistem penguat internal yang memperkuat lapisan es dari dalam. Pembentukan lattice ini melibatkan proses kristalisasi ulang dan interaksi molekuler air laut dengan es yang jauh lebih kompleks daripada yang dipahami sebelumnya.

Penemuan crystal reinforcement lattice sendiri memunculkan harapan baru dalam memahami mekanisme alami pelindung bagi ice shelf dari keretakan dan kerusakan akibat meningkatnya suhu dan arus laut yang kuat. Dalam konteks riset es laut yang saat ini sedang berlangsung, fenomena ini dianggap sebagai jawaban Continue reading