If you run a self-hosted Ubiquiti UniFi network — whether it’s a home lab, small business, or multi-site setup — you know the UniFi dashboard is great for real-time monitoring but falls short when you want a clean summary you can save, share, or review later. I built UniFi Network Health Report to fill that...
On April 29, 2026, a Linux kernel local privilege escalation vulnerability was publicly disclosed under the name "Copy Fail" (CVE-2026-31431). Cloudflare’s Security and Engineering teams began assessing the vulnerability as soon as it was disclosed. We reviewed the exploit technique, evaluated exposure across our infrastructure, and validated that our existing behavioral detections could identify the exploit pattern within minutes.
There was no impact to the Cloudflare environment, no customer data was at risk, and no services were disrupted at any point. Read on to learn how our preparedness paid off.
Background
Our Linux kernel release process
Cloudflare operates a global Linux server infrastructure at an immense scale, with datacenters located across 330 cities. We maintain a custom Linux kernel build based on the community's Long-Term Support (LTS) versions to manage updates effectively at this volume. At any given time, we may utilize multiple LTS versions from various series, such as 6.12 or 6.18, which benefit from extended update periods.
The community regularly merges and releases security and stability updates which trigger an automated job to generate a new internal kernel build approximately every week. These builds undergo testing in our staging data centers to Continue reading
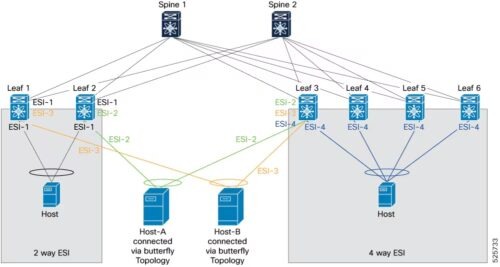
For years, multi-homing in VXLAN BGP/EVPN fabrics with Cisco Nexus switches meant one thing: vPC. It works very well; two-switch redundancy, familiar operational model, no need to deeply understand EVPN’s…
For years, multi-homing in VXLAN BGP/EVPN fabrics with Cisco Nexus switches meant one thing: vPC. It works very well; two-switch redundancy, familiar operational model, no need to deeply understand EVPN’s…
Eric Chou talks with Adrian Iliesiu aka NetGru, a seasoned CCIE veteran and community leader known for his work to simplify network automation and make it accessible to network engineers. He focuses on helping network teams navigate the transition into AI and vibe coding while maintaining their core technical skills. Adrian shares insights and practical... Read more »
Eyvonne and William sit down with Joseph Nicholson, a Network Operations Engineer with NTT DATA, to share how public speaking transformed his career and technical experience. Joseph went from a terrifying ten minute lightning talk at AutoCon 2 to presenting 45-minute sessions at conferences like NANOG. Together they discuss how conversations in conference halls influenced... Read more »
On May 5, 2026, at roughly 19:30 UTC, DENIC, the registry operator for the .de country-code top-level domain (TLD), started publishing incorrect DNSSEC signatures for the .de zone. Any validating DNS resolver receiving these signatures was required by the DNSSEC specification to reject them and return SERVFAIL to clients, including 1.1.1.1, the public DNS resolver operated by Cloudflare.
The country-code top-level domain for Germany, .de, is one of the largest on the Internet. On Cloudflare Radar, it consistently ranks among the most broadly queried TLDs globally. An outage at this level of the DNS hierarchy has the potential to make millions of domains unreachable.
In this post, we’ll walk through what we saw, the impact of these events, and how we applied temporary mitigations while DENIC resolved the issue.
How DNSSEC works
DNSSEC (Domain Name System Security Extensions) adds cryptographic authentication to DNS. When a zone is signed with DNSSEC, each set of records is accompanied by a digital signature known as an RRSIG record that lets a resolver verify the records haven’t been tampered with. Unlike encrypted DNS protocols, such as DNS over TLS (DoT) and DNS over HTTPs (DoH), DNSSEC is about Continue reading
Why You Should Attend Cisco Live — and Actually Talk to People Back in 2022, I wrote a post covering everything Cisco Live has to offer: the technical sessions, the…
Why You Should Attend Cisco Live — and Actually Talk to People Back in 2022, I wrote a post covering everything Cisco Live has to offer: the technical sessions, the…
A while ago, I found the How Automatic Return Routing solves IP overlap article on Cloudflare’s blog. They evidently have a technology that addresses a pain point well worth solving (access to shared resources from clients using overlapping address ranges). I just hate how they’re selling it. Go read the article first; I’ll wait.
OK, here’s what bothers me: the “VRFs and NAT are bad” claims, while they use the same technology in disguise.
It was 11:47pm on a Thursday night, and a senior platform engineer at a large North American bank was rolling back a ‘simple’ configuration change. The change itself was small, a routine update approved through the usual review process, but when it was applied, pods began cycling and connections started dropping. For the next three seconds, mobile banking sessions already mid-transaction dropped. Customer support lit up. The incident review the next morning spent most of its time arguing about how the change had been approved. Almost no one asked the harder question: why a configuration change in one place broke something seemingly unrelated.
That question rarely gets a clean answer. What looks like a single layer is usually one knot in a stack of five to seven products including a CNI, network policy, service mesh, observability, threat detection and compliance tooling that come from different vendors and were never designed to operate as one system. Each one works. The gaps between them are where the risk, and the cost, lives.
This is just one example of the Kubernetes integration tax.
What is the Kubernetes Integration Tax?
The Kubernetes integration tax is the cumulative cost in engineer time, security exposure, Continue reading
In this sponsored episode, brought to you by Cisco, Keith sits down with Mark Rodrigue of Room & Board and Dan Davis of Cisco. They discuss Room & Board’s network and how their three-person networking team manages over 700 access points with the help of Meraki Cloud Management. Room & Board’s story is a great... Read more »
In theory, a zero trust initiative seems straightforward: you just need the right tools and maybe some whiteboard sessions to work out the architecture. In practice, our guests note that zero trust “unfolds inside organizations filled with legacy systems, political friction, budget constraints, and competing priorities.” Without accounting for those complications, a zero trust project... Read more »
Enterprise strategists need to worry about securing their environments against AI-powered attacks. John and Johna discuss what cybersecurity and IT leaders need to consider in developing a cybersecurity strategy that addresses AI-augmented threats as well as how to use AI defensively … and why AI attacks can be like a duckbilled platypus. AdSpot Sponsor: Meter... Read more »