SPONSORED It is only natural the world’s top supercomputing sites in climate and weather modeling should be leading the charge for more efficient, sustainable, and green datacenter practices. …
Angelo Rossi, GNS LAN-WAN Architect at WSP joins Drew Conry-Murray of the Packet Pushers to explain how WSP automated their brownfield network with Gluware. If Gluware might be a fit for your network automation needs, visit here. Thanks! You can subscribe to the Packet Pushers’ YouTube channel for more videos as they are published. It’s […]
Today we’re announcing a public demo and an open-sourced Go implementation of a next-generation, privacy-preserving compromised credential checking protocol called MIGP (“Might I Get Pwned”, a nod to Troy Hunt’s “Have I Been Pwned”). Compromised credential checking services are used to alert users when their credentials might have been exposed in data breaches. Critically, the ‘privacy-preserving’ property of the MIGP protocol means that clients can check for leaked credentials without leaking any information to the service about the queried password, and only a small amount of information about the queried username. Thus, not only can the service inform you when one of your usernames and passwords may have become compromised, but it does so without exposing any unnecessary information, keeping credential checking from becoming a vulnerability itself. The ‘next-generation’ property comes from the fact that MIGP advances upon the current state of the art in credential checking services by allowing clients to not only check if their exact password is present in a data breach, but to check if similar passwords have been exposed as well.
For example, suppose your password last year was amazon20\$, and you change your password each year (so your current password is amazon21\$). Continue reading
At large operational scales, IP addressing stifles innovation in network- and web-oriented services. For every architectural change, and certainly when starting to design new systems, the first set of questions we are forced to ask are:
Which block of IP addresses do or can we use?
Do we have enough in IPv4? If not, where or how can we get them?
How do we use IPv6 addresses, and does this affect other uses of IPv6?
Oh, and what careful plan, checks, time, and people do we need for migration?
Having to stop and worry about IP addresses costs time, money, resources. This may sound surprising, given the visionary and resilient advent of IP, 40+ years ago. By their very design, IP addresses should be the last thing that any network has to think about. However, if the Internet has laid anything bare, it’s that small or seemingly unimportant weaknesses — often invisible or impossible to see at design time — always show up at sufficient scale.
One thing we do know: “more addresses” should never be the answer. In IPv4 that type of thinking only contributes to their scarcity, driving up further their market prices. IPv6 is absolutely necessary, Continue reading
As Internet users, we all deal with passwords every day. With so many different services, each with their own login systems, we have to somehow keep track of the credentials we use with each of these services. This situation leads some users to delegate credential storage to password managers like LastPass or a browser-based password manager, but this is far from universal. Instead, many people still rely on old-fashioned human memory, which has its limitations — leading to reused passwords and to security problems. This blog post discusses how Cloudflare Research is exploring how to minimize password exposure and thwart password attacks.
The Problem of Password Reuse
Because it’s too difficult to remember many distinct passwords, people often reuse them across different online services. When breached password datasets are leaked online, attackers can take advantage of these to conduct “credential stuffing attacks”. In a credential stuffing attack, an attacker tests breached credentials against multiple online login systems in an attempt to hijack user accounts. These attacks are highly effective because users tend to reuse the same credentials across different websites, and they have quickly become one of the most prevalent types of online guessing attacks. Automated attacks can be run Continue reading
Thomas Kurian’s arrival at Google Cloud in early 2019 after more than 22 years at Oracle marked a significant shift in Google’s thinking, putting an emphasis on expanding its cloud’s business use by enterprises as the key to making up ground on Amazon Web Services (AWS) and Microsoft Azure in the booming global cloud market. …
Almost a decade ago I described a scenario in which a perfectly valid IBGP topology could result in a permanent routing loop. While one wouldn’t expect to see such a scenario in a well designed network, it’s been known for ages1 that using BGP route reflectors could result in suboptimal forwarding.
Here’s a simple description of how that could happen:
Almost a decade ago I described a scenario in which a perfectly valid IBGP topology could result in a permanent routing loop. While one wouldn’t expect to see such a scenario in a well designed network, it’s been known for ages1 that using BGP route reflectors could result in suboptimal forwarding.
Here’s a simple description of how that could happen:
Tina Peters, the elections clerk from Mesa County (Colorado) went rogue, creating a "disk-image" of the election server, and posting that image to the public Internet. Conspiracy theorists have been analyzing the disk-image trying to find anomalies supporting their conspiracy-theories. A recent example is this "forensics" report. In this blogpost, I debunk that report.
I suppose calling somebody a "conspiracy theorist" is insulting, but there's three objective ways we can identify them as such.
The first is when they use the logic "everything we can't explain is proof of the conspiracy". In other words, since there's no other rational explanation, the only remaining explanation is the conspiracy-theory. But there can be other possible explanations -- just ones unknown to the person because they aren't smart enough to understand them. We see that here: the person writing this report doesn't understand some basic concepts, like "airgapped" networks.
This leads to the second way to recognize a conspiracy-theory, when it demands this one thing that'll clear things up. Here, it's demanding that a manual audit/recount of Mesa County be performed. But it won't satisfy them. The Maricopa audit in neighboring Colorado, whose recount found no fraud, didn't clear anything up Continue reading
Ex-Nervana Systems engineers made the jump from a hardware-centric approach to efficient training to pushing better insight into optimization of models and systems.…
Automation is often put forward as the answer to all our problems—but without a map, how can we be certain we are moving in the right direction? David Gee joins Tom Ammon and Russ White on this episode of the Hedge to talk about automata without a map. Where did we come from, what are we doing with automation right now, and what do we need to do to map out a truly better future?
Search engine and cloud computing juggernaut Google is hosting its Google Cloud Next ’21 conference this week, and one of the more interesting things that the company unveiled is several layers of software that makes its Spanner globally distributed relational database look and feel like the popular open source PostgreSQL relational database. …
Marvell has begun to sample the Octeon 10, a server microprocessor aimed at intelligent network management that has up to 24 Arm-compatible cores, making it as powerful as any server processor.Marvell refers to the Octeon processor line as data processing units (DPUs). They are designed to run high-throughput data in the cloud and on-premises. The DPU is more commonly called the SmartNIC because it can offload non-computational tasks from the CPU like network packet processing, data encryption and compression. That frees up CPU cores to run general-purpose applications.The Octeon 10 has a few firsts. It's the first processor made by TSMCs 5nm manufacturing process and the first processor to feature Arm’s Neoverse N2 core. The N2 core uses the new Armv9 architecture that the company claims can deliver 40% more single-threaded performance for a variety of workloads vs. the N1, but still retains the same level of power and area efficiency as N1.To read this article in full, please click here
Ethan Banks & Ned Bellavance have a tech discussion with CEO Doug Murray and CTO Vishal Jain about multi-cloud security startup Valtix. Along the way, we find out that Valtix is a cloud-delivered security control-plane paired with a data-plane of enforcement points (sort of firewalls, but not exactly) delivered between any two points in the cloud you need them. Engineers should walk away from this chat with a solid idea of Valtix architecture and how it fits into their cloud design.
Ethan Banks & Ned Bellavance have a tech discussion with CEO Doug Murray and CTO Vishal Jain about multi-cloud security startup Valtix. Along the way, we find out that Valtix is a cloud-delivered security control-plane paired with a data-plane of enforcement points (sort of firewalls, but not exactly) delivered between any two points in the cloud you need them. Engineers should walk away from this chat with a solid idea of Valtix architecture and how it fits into their cloud design.
The third-placed cloud vendor has announced a new set of options for customers that need to keep certain workloads in self-hosted environments or out at the edge.
Axway CTIO Vince Padua believes the best path forward is to master growing API complexity, rather than attempt to simplify or consolidate IT ecosystems.
The Internet, far from being just a series of tubes, is a huge, incredibly complex, decentralized system. Every action and interaction in the system is enabled by a complicated mass of protocols woven together to accomplish their task, each handing off to the next like trapeze artists high above a virtual circus ring. Stop to think about details, and it is a marvel.
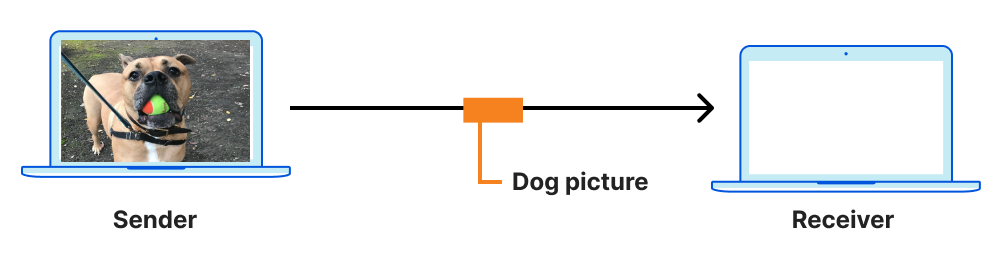
Consider one of the simplest tasks enabled by the Internet: Sending a message from sender to receiver.
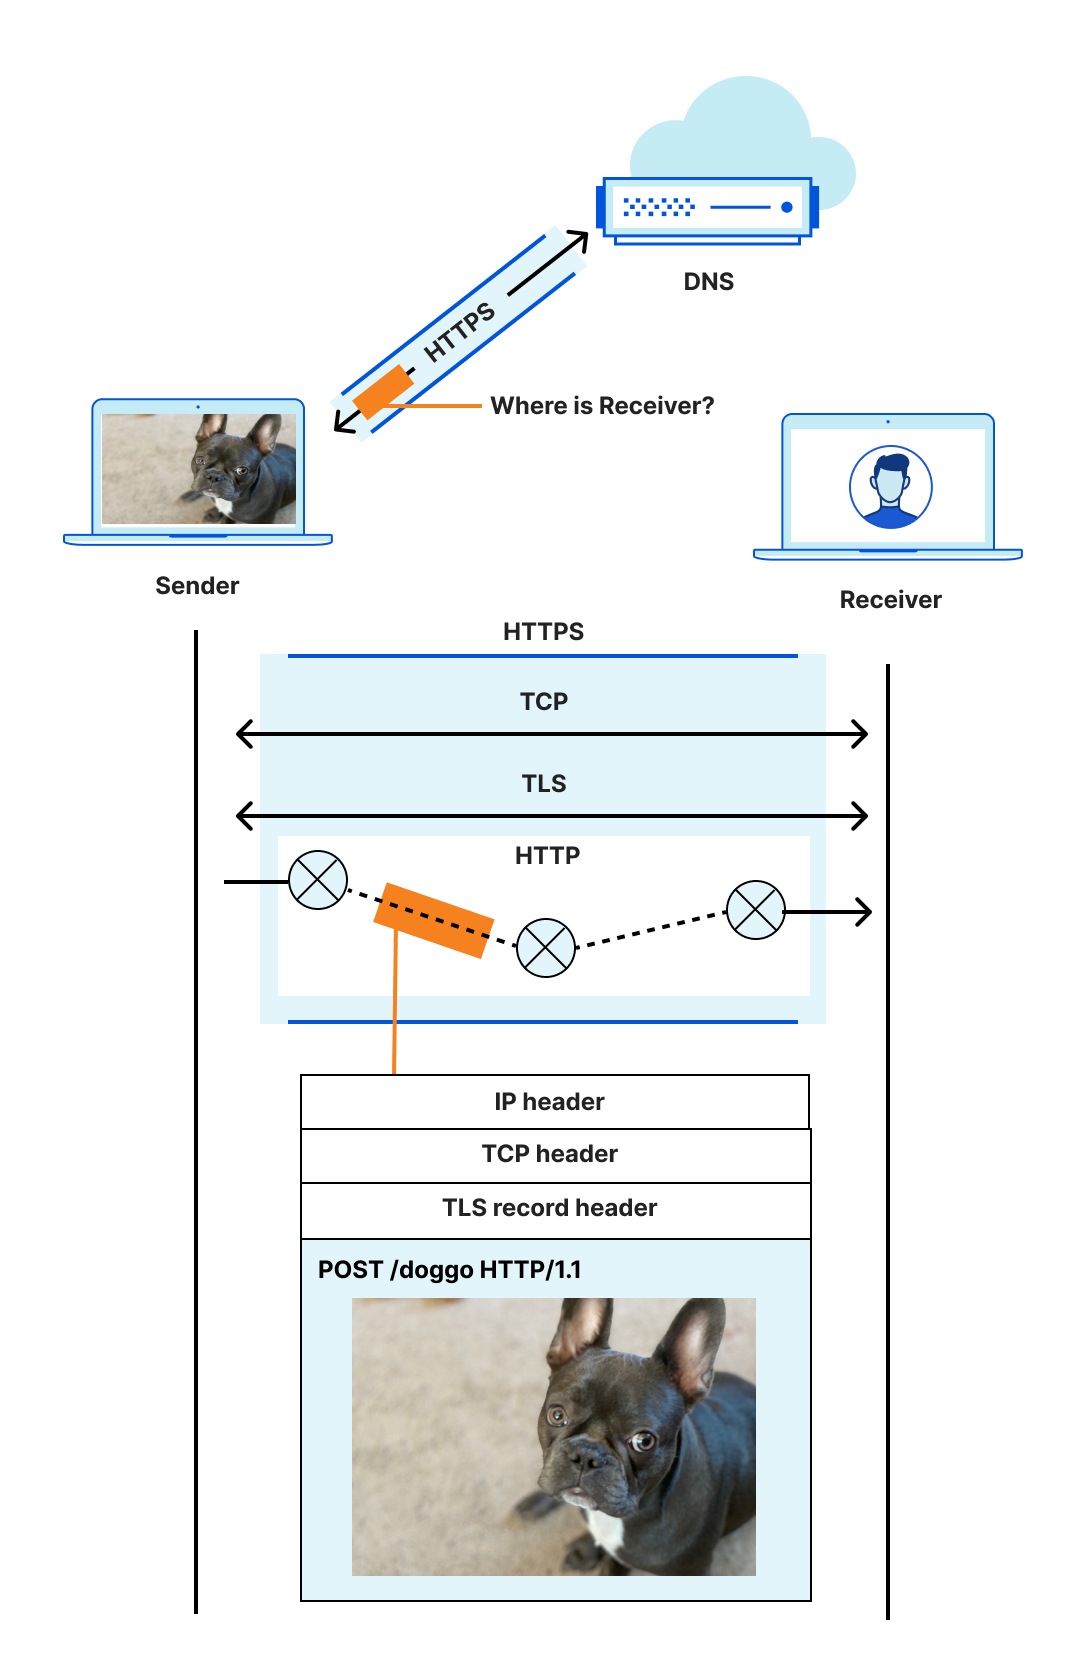
The location (address) of a receiver is discovered using DNS, a connection between sender and receiver is established using a transport protocol like TCP, and (hopefully!) secured with a protocol like TLS. The sender's message is encoded in a format that the receiver can recognize and parse, like HTTP, because the two disparate parties need a common language to communicate. Then, ultimately, the message is sent and carried in an IP datagram that is forwarded from sender to receiver based on routes established with BGP.
Even an explanation this dense is laughably oversimplified. For example, the four protocols listed are just the start, and ignore many others with acronyms of their own. The truth is that things are complicated. Continue reading
In 2019, we announced the release of CIRCL, an open-source cryptographic library written in Go that provides optimized implementations of several primitives for key exchange and digital signatures. We are pleased to announce a major update of our library: we have included more packages for elliptic curve-based cryptography (ECC), pairing-based cryptography, and quantum-resistant algorithms.
In this blog post we’re going to focus on pairing-based cryptography and give you a brief overview of some properties that make this topic so pleasant. If you are not so familiar with elliptic curves, we recommend this primer on ECC.
Otherwise, let’s get ready, pairings have arrived!
What are pairings?
Elliptic curve cryptography enables an efficient instantiation of several cryptographic applications: public-key encryption, signatures, zero-knowledge proofs, and many other more exotic applications like oblivious transfer and OPRFs. With all of those applications you might wonder what is Continue reading