Why Is My Switch Still Red? The Future of Network Switches
Rethinking Network Switches The rate of technological change today can seem overwhelming but if you are old enough, you start to realize its pretty much more of the same. My biggest fear with tech change is that I don't want it to happen TO me. I may not be in a position to be in READ MORE
The post Why Is My Switch Still Red? The Future of Network Switches appeared first on The Gratuitous Arp.
Hedge 317: AI Tools and Coding

How effective are AI tools–even agentic AI tools placed into a system–at building and testing software? Derick Winkworth and Donald Sharp Join Russ to discuss various projects they’ve worked on using AI tools, lessons they’ve learned, and how developers can make effective use of AI.
download
TNO070: Spec Driven Design (SDD) for NetOps and NetEng
NetOps engineer Lasse Haugen sits down with Scott Robohn at AutoCon 5 to explore the power of Spec Driven Design (SDD) for transforming network engineering workflows from chaotic experimentation to structured, reliable automation. Together they define what SDD is, use cases for NetOps and NetEng, how it has changed NetOps, and more. AdSpot Sponsor: NANOG,... Read more »HN839: Why Flows, Packets, and DDI are All Critical for Operational Effectiveness (Sponsored)
If you think of BlueCat as just an IPAM or DDI company, think again. BlueCat acquired LiveAction in 2024, and since then, they’ve been working to integrate LiveAction’s network observability capabilities with the DDI portfolio. In this sponsored episode, Ryan Grande, Field CTO at BlueCat, is here to dig into how network observability and DDI... Read more »BotBase for Operators: A clearer path to joining Cloudflare’s directory of bots and agents
Last month, on our second Content Independence Day, we announced a couple of features designed to give website owners more visibility and control over automated traffic: BotBase added a searchable directory of known bots to the Cloudflare dashboard, while Business Insights helped owners understand how crawlers interact with their content. We know that the ecosystem of bots is vast, making it all the more important for site owners to be able to manage bot traffic sustainably.
But this ecosystem goes both ways. While website owners need to decide which automated traffic they allow, bot operators need a clear way to identify themselves, explain what their bots do, and keep that information current. BotBase works best when both sides can participate.
When we launched BotBase, we said we would build tools to bring bot operators into this ecosystem. Until now, their experience largely ended at submission. After pressing submit, an operator had no easy way to check the submission's status, understand why it was rejected, or update an existing entry. Today, we start to change that with the launch of BotBase for Operators, tackling what bot operators need first: transparency.
A new home for bot submissions
Imagine you’re a bot operator Continue reading
Using netlab in Software Testing with Dinesh Dutt
I know a few software development companies use netlab to test their network management software (and contribute back to netlab – thanks a million!), and I always wanted to chat about that. As I have known Dinesh Dutt for ages, it wasn’t hard to decide who to invite to have that chat with ;)
As it turns out, it’s dangerous to put Dinesh1 and me in the same (virtual) room – we were all over the place, from the ancient history of Vagrant in networking labs to the recent Ansible woes, but we did manage to cover how netlab helps Stardust Systems test new SuzieQ features.
The Safest Place to Run an AI Agent Is On a Cluster That Doesn’t Trust It
Every organization running AI agents has already made a hosting decision. Most made it by accident.
The sales team switched on the agent built into their CRM. Engineering is piloting a coding agent in a vendor’s cloud. Someone on the data team deployed a LangGraph service to a VM with a database key in an environment variable, and someone else is running an agent framework on a laptop with production credentials in a dotfile. Each of these is a hosting decision. Each one quietly settled who holds the agent’s credentials, what network paths it can reach, what gets recorded when it acts, and who can stop it. Nobody ran an architecture review, because no single deployment looked big enough to deserve one.
The scale says otherwise. By May 2025, 82% of organizations surveyed by SailPoint were already using AI agents. Only 44% had policies for securing them, 80% said their agents had already taken unintended actions, and 23% had watched an agent get tricked into revealing credentials. A year later the bill arrived: IBM’s 2026 Cost of a Data Breach report found that one in four malicious breaches is now AI-enabled, up 56% in a single year, and that those Continue reading
LIU021: Justin Ryburn – The Road More Traveled with a Field CTO
Kevin and Alexis welcome Justin Ryburn, VP of Global Solution Engineering and Field CTO at Kentik, to discuss the realities of traveling for technical work. Justin explains the nuances of his role, which balances executive engagement, public speaking, and team leadership with the challenge of a heavy travel schedule. They also touch on the importance... Read more »How we saved 100 terabytes of memory by optimizing 1.1.1.1’s DNS cache
Big Pineapple, the platform behind 1.1.1.1, Gateway DNS, DNS Firewall, AS112, and several other Cloudflare DNS services, stores over 250 billion DNS cache entries at any given time. At that scale, wasting a single byte per entry costs more than 250 gigabytes of memory across our fleet.
Five successive changes to how cache entries are stored in memory cut the per-entry footprint by over 50%. Across our fleet, these changes freed up roughly 100 terabytes of memory, equivalent to the amount of RAM in 130 of our Gen 13 servers. The cache also got faster. Insert throughput rose 43% and lookup latency dropped 19%, as fewer allocations and better memory locality meant we did not trade speed for space.
What we cache
On cold start, Big Pineapple starts out with an empty cache. As DNS queries arrive, the cache fills until it hits its maximum entry count, at which point we evict older or less popular items to make room.
The exact cache size varies by data center. When EDNS Client Subnet (ECS) is in use, authoritative servers return different answers depending on the client's network, so we cache multiple versions of Continue reading
Yak-Shaving netlab Podman Support
Long, long time ago, in a long-forgotten PR adding support for Cumulus VX Ignite runtime, an off-the-cuff remark was made saying, “and this is how you use netlab with Podman”. That remark was quietly sitting in the documentation for years until someone (A) tried to use Podman and (B) found enough time to report that it doesn’t work with netlab.
I don’t know what that tells us: either very few people use Podman, or nobody (apart from a notable exception) cares enough to spend a few minutes telling us stuff doesn’t work1.
Anyway, based on Joey Buiteweg’s wonderful research, I was able to put together a working solution pretty quickly, but it did involve a lot of yak shaving (more bovine details).
D2DO311: Code Review Is Dead – Long Live Peer Review
Traditional peer review processes are breaking down in the new AI era. Dylan Ratcliffe, founder and CEO of Overmind Technology, joins Ned and Kyler to discuss the importance of treating AI as a machine to be audited rather than a peer. Together they share practical advice on how to adapt peer review processes and culture... Read more »Dear Junos, Tunnels Are Not Virtual Links
In late June, we added GRE tunnels to netlab, including a Junos implementation. It looked great (as in “everything worked”) until I changed the integration tests to have GRE tunnels between a tested device and a pair of FRR containers. All other implementations worked as before, but Junos failed to establish an OSPFv3 adjacency over the GRE tunnel with FRR.
Stefano Sasso quickly identified the culprit: Junos OSPFv3 process thinks it should send the DBD packets over GRE tunnels with MTU set to zero (the behavior reserved for virtual links)1.
Testing DDoS mitigation software

The screen capture shows how sflowgen DDoS attack telemetry appears in the DDoS Protect dashboard. Charts in the dashboard show different types of DDoS attack. You can see normal low level background activity below the red horizontal threshold line. DDoS traffic can be seen ramping up on the udp_flood and ip_flood charts and leveling off once the attack reaches maximum intensity. Notice that as soon as the attack traffic crosses the threshold, the Controls chart indicates that a Pending control has been created to mitigate the attack.


The Settings tab has been configured to add a local address group containing the 10.10.0.0/24 and 2001:db8:10::/64 CIDRs used in the default Continue reading
PP123: Using Gridctl to Keep MCP Configs From Leaking Secrets
If you’ve been spinning up AI tools — Claude Desktop, Cursor, Copilot, and so on — there’s a decent chance that API keys, credentials, and access tokens are sitting in plaintext on your laptop. With MCP, every quickstart guide tells you to paste your credentials right into a config file. That was a bad habit... Read more »HW086: High Density Wi-Fi Part 2
By popular demand, Keith is joined once again by Ferney Muñoz and Tom Hildebrand to answer listener questions and to dive deeper into designing high-density Wi-Fi for large-scale events. Together they share practical insights on managing DHCP scopes, the realities of client isolation, and more.Multivendor SR-MPLS
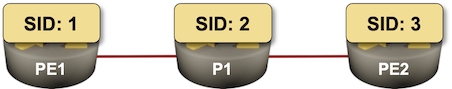
Summer is almost over, and it’s time to resume regular programming with the next example from the Segment Routing workshop I had at ITNOG10: multi-vendor SR-MPLS. I used the same lab topology as in the previous examples but deployed Arista EOS on PE1, FRRouting on P, and SR Linux on PE21
The Cloudflare Blog – Brought to you by EmDash
You likely noticed the recent redesign of the Cloudflare Blog. We added dark mode, modernized the look and feel, and made a lot of other small improvements along the way.
What you might not have noticed – well, except for those who are more terminally online – is that the redesign was part of a much bigger migration project. On Wednesday, August 12, we moved the blog to EmDash, a content management system (CMS) built especially to work on Astro and with Cloudflare.
We’ll take you into the migration story – what we learned and how EmDash got better – as well as into the benefits we’re already seeing from a new platform.
We are Customer Zero
At Cloudflare, Cloudflare itself is Customer Zero. This means that we use our products. And – in use – we make them better for ourselves and our customers.
This is a very real cultural value at Cloudflare. The burden of proof is on you if you want to use an external vendor. Why can’t that team support you, what gaps are there, why can’t those gaps be filled, and are those “gaps” true requirements?
This preference is even enshrined in our internal Continue reading
NB588: Active Threats Target Siemens PLCs; IBM Chills Qubits With Modular Cryogenics
Take a Network Break! It’s a Red Alert double feature for Oracle’s Internet Directory LDAP server and Cisco’s Secure Workload Software. In tech news, US law enforcement and intelligence agencies release a joint advisory warning of active threats against Siemens PLCs, Marvell wins a deal to make chips for Google that could bring billions in... Read more »An interactive introduction to the spanning tree protocol
Warning
This post contains interactive examples. To visualize and interact with them, you need to leave your RSS reader.
Imagine you rent office space for a three-day event. You quickly set up a few Ethernet switches and tape some cables on the floor to get everyone online. Unfortunately, Stan, your clumsiest coworker, kicks out a cable every time he gets up for coffee. You could add extra cables, but then you’d get a broadcast storm: Ethernet packets that loop and multiply until nothing else gets through.
That’s where the spanning tree protocol (STP) comes in. STP blocks just enough of your spare cables to leave a loop-free tree. When Stan strikes again, it rebuilds the tree in a second, leaving some time for Blobby, your one-person support crew, to reconnect the cable. See for yourself: the diagram below runs a real STP implementation in your browser!
:demo

A1 @0,0 prio=4096
A2 @0,1
A3 @0,2
A4 @0,3

B1 @1,0 prio=8192
B2 @1,1
B3 @1,2
B4 @1,3

C1 @2,0 prio=8192
C2 @2,1
C3 @2,2
C4 @2,3

A1 -- A2 hazard=0
A2 -- A3 hazard=0
A3 -- A4 hazard=0
B1 -- B2
B2 -- B3
B3 -- B4
C1 -- C2 Continue readingA non-interactive introduction to the spanning tree protocol
Imagine you rent office space for a three-day event. You quickly set up a few Ethernet switches and tape some cables on the floor to get everyone online. Unfortunately, Stan, your clumsiest coworker, kicks out a cable every time he gets up for coffee. Spare cables would fix that, but a loop turns into a broadcast storm: Ethernet packets multiply until nothing else gets through. That’s where the spanning tree protocol comes in: it blocks just enough of the spare cables to leave a loop-free tree, and rebuilds it in a second each time Stan strikes again.
This content is also available as a text version, with interactive demos that run a real implementation directly in your browser!
This video is an experiment.1 Honestly, except for Radia Perlman reading her poem,2 you should read the original article instead. It presents the same content, but you can play with the interactive examples, which are the main contribution. On the other hand, if you happen to like the video, be sure to tell me in the comments!
-
I thought automated tools would produce this video in a couple of hours. In the end, it was another rabbit hole Continue reading