BGPSec – A reality now
 The Secure Inter Domain Routing (SIDR) initiative held its first BoF at IETF 64 back in November 2005, and was established as a Working Group in April 2006. Following the Youtube Hijack incident in 2008, the need to secure BGP became increasingly important and SIDR WG charter explains it well:
The purpose of the SIDR working group is to reduce vulnerabilities in the inter-domain routing system. The two vulnerabilities that will be addressed are:
- Is an Autonomous System (AS) authorized to originate an IP prefix
- Is the AS-Path represented in the route the same as the path through which the NLRI traveled.
This last vulnerability was the basis for defining an AS Path validation specification which has become known as BGPsec.
BGPsec attempts to assure a BGP peer that the content of a BGP update it has received, correctly represents the inter-AS propagation path of the update from the point of origination to the receiver of the route.
So far, 39 RFCs have originated from the SIDR WG, with three drafts currently under discussion. Seven RFCs were published last month (September 2017) providing a big boost to the securing routing work:
- RFC 8205 (was draft-ietf-sidr-bgpsec-protocol) – BGPsec Protocol Specification
- RFC 8206 Continue reading


 Juniper cuts Q3 forecasts; Vodafone exec calls for vendors to collaborate; and ETSI to connect NFV and OSS.


 Company claims breadth and depth of its platform differentiates it from rivals.

 “Our goal is abundant bandwidth for everyone.”
 Enterprises selected IoT vendors based on price, robustness of technology, and vendor knowledge.
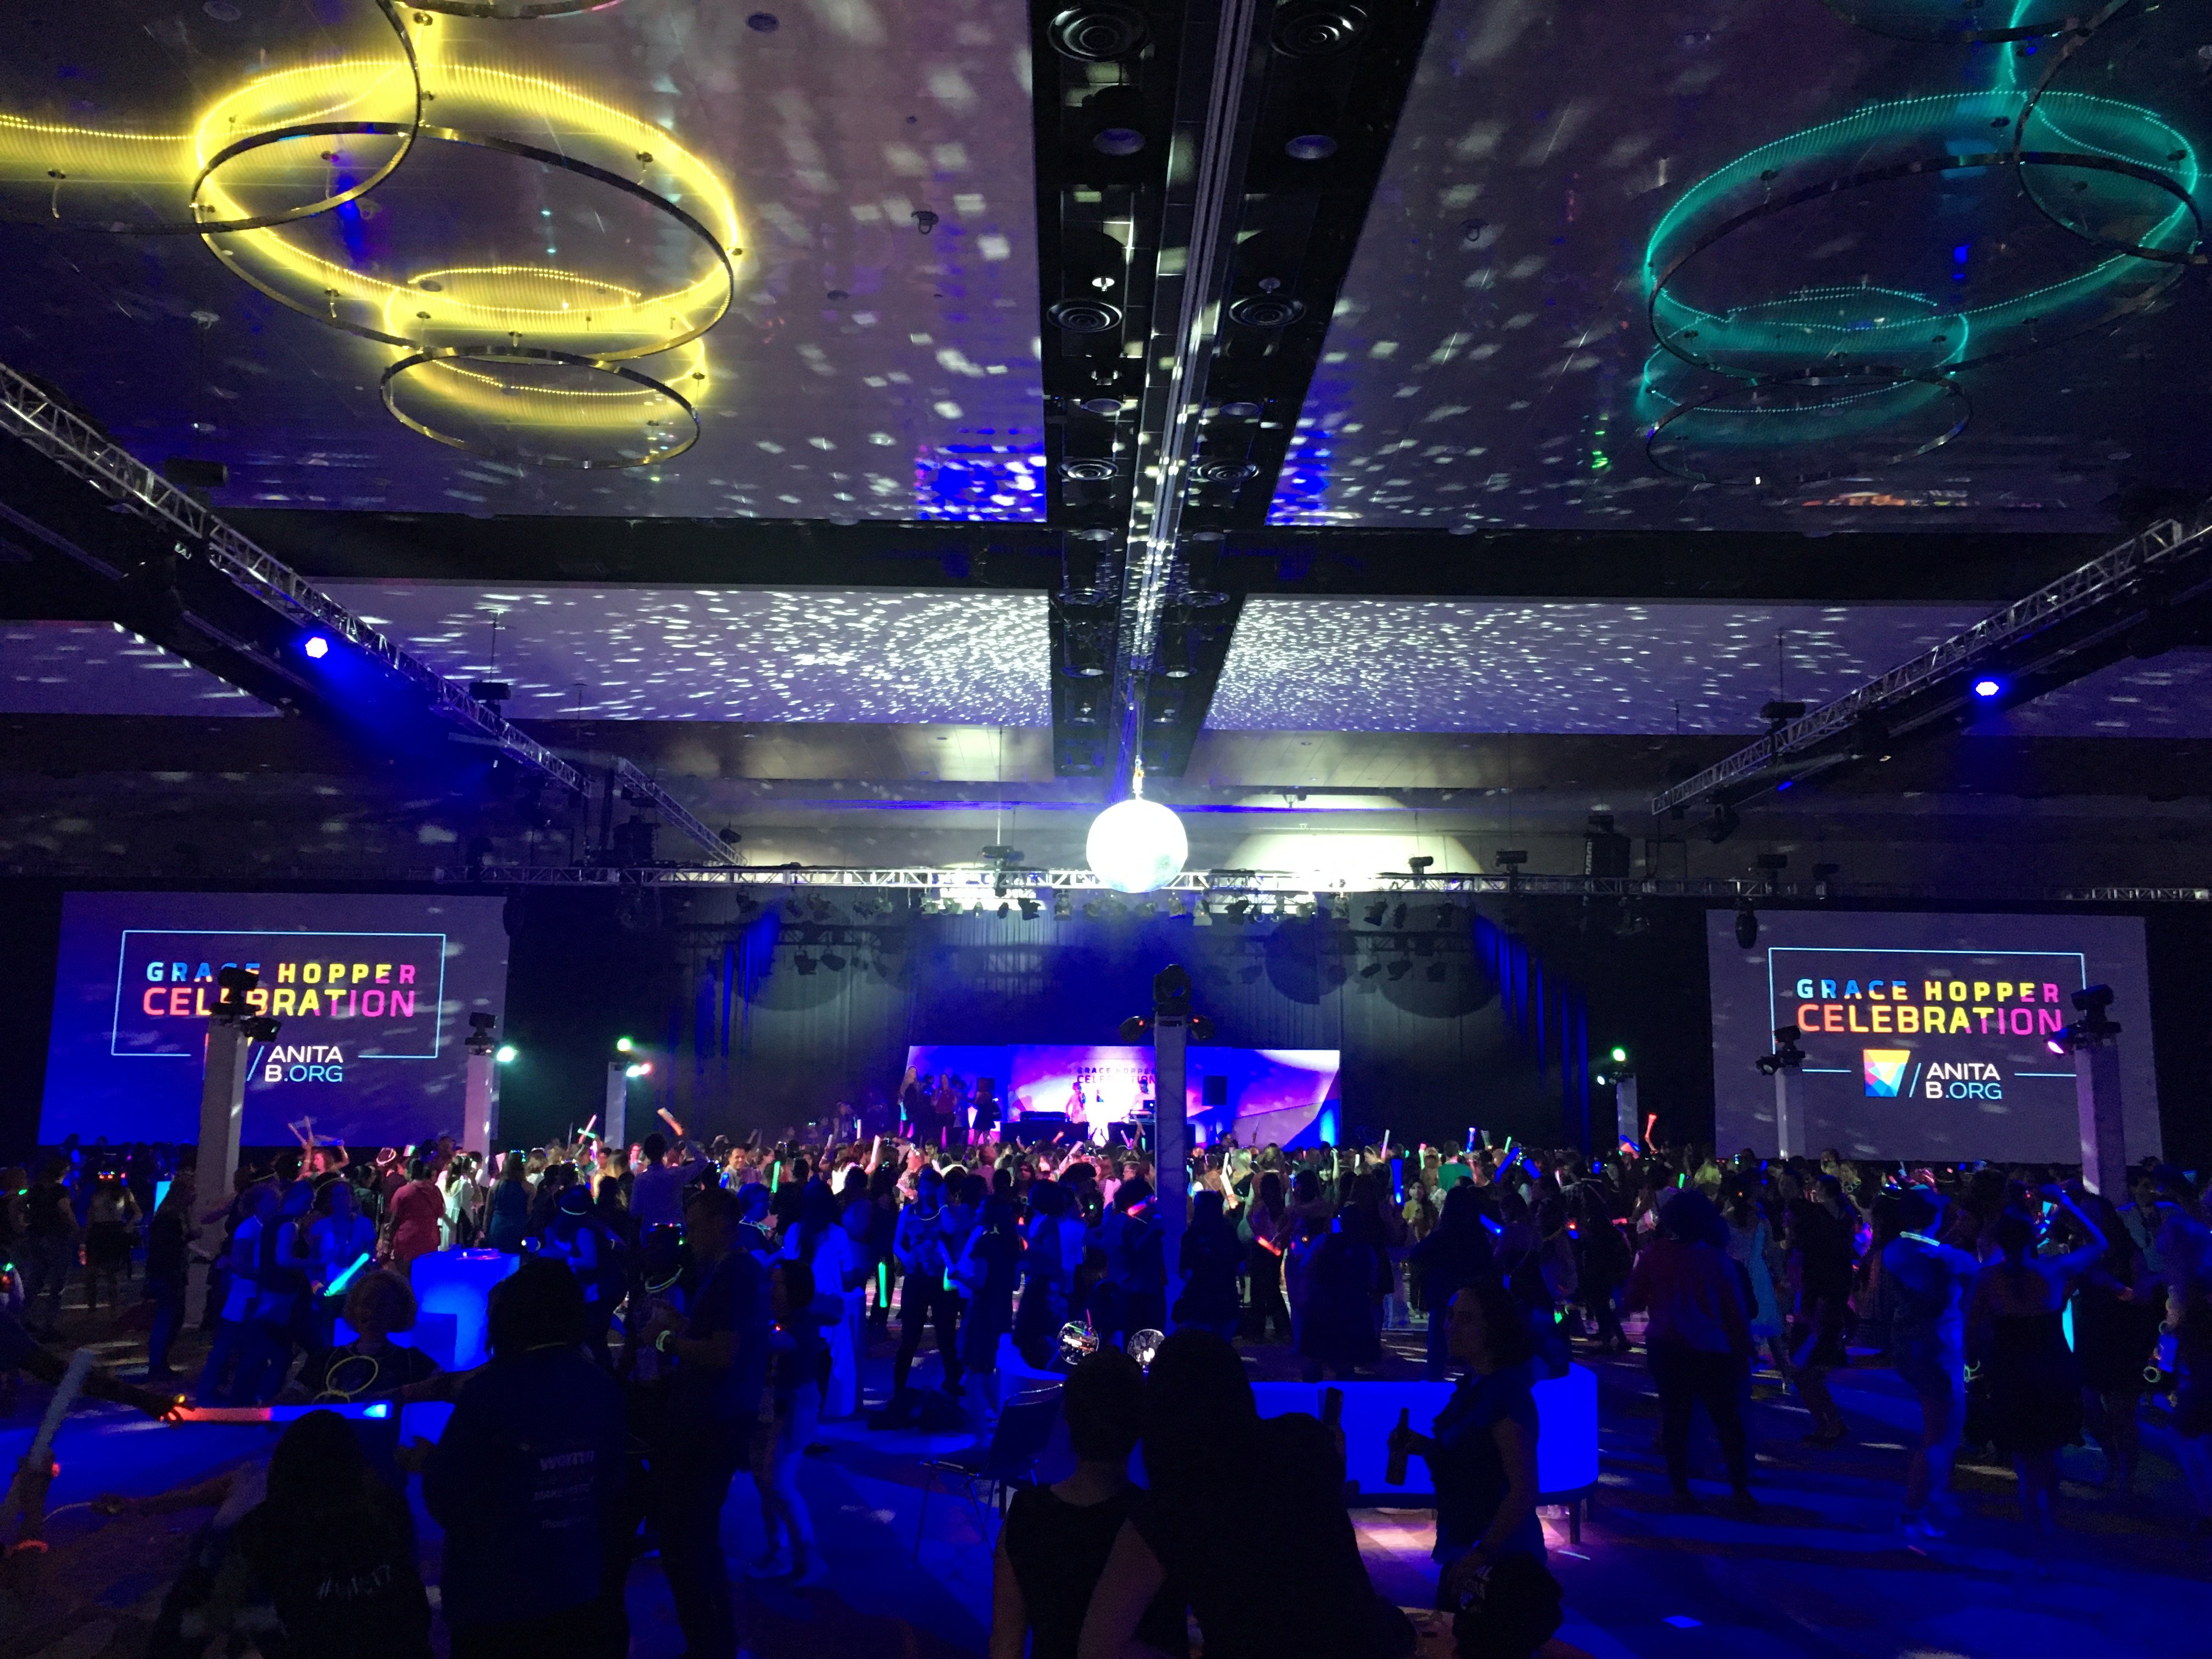
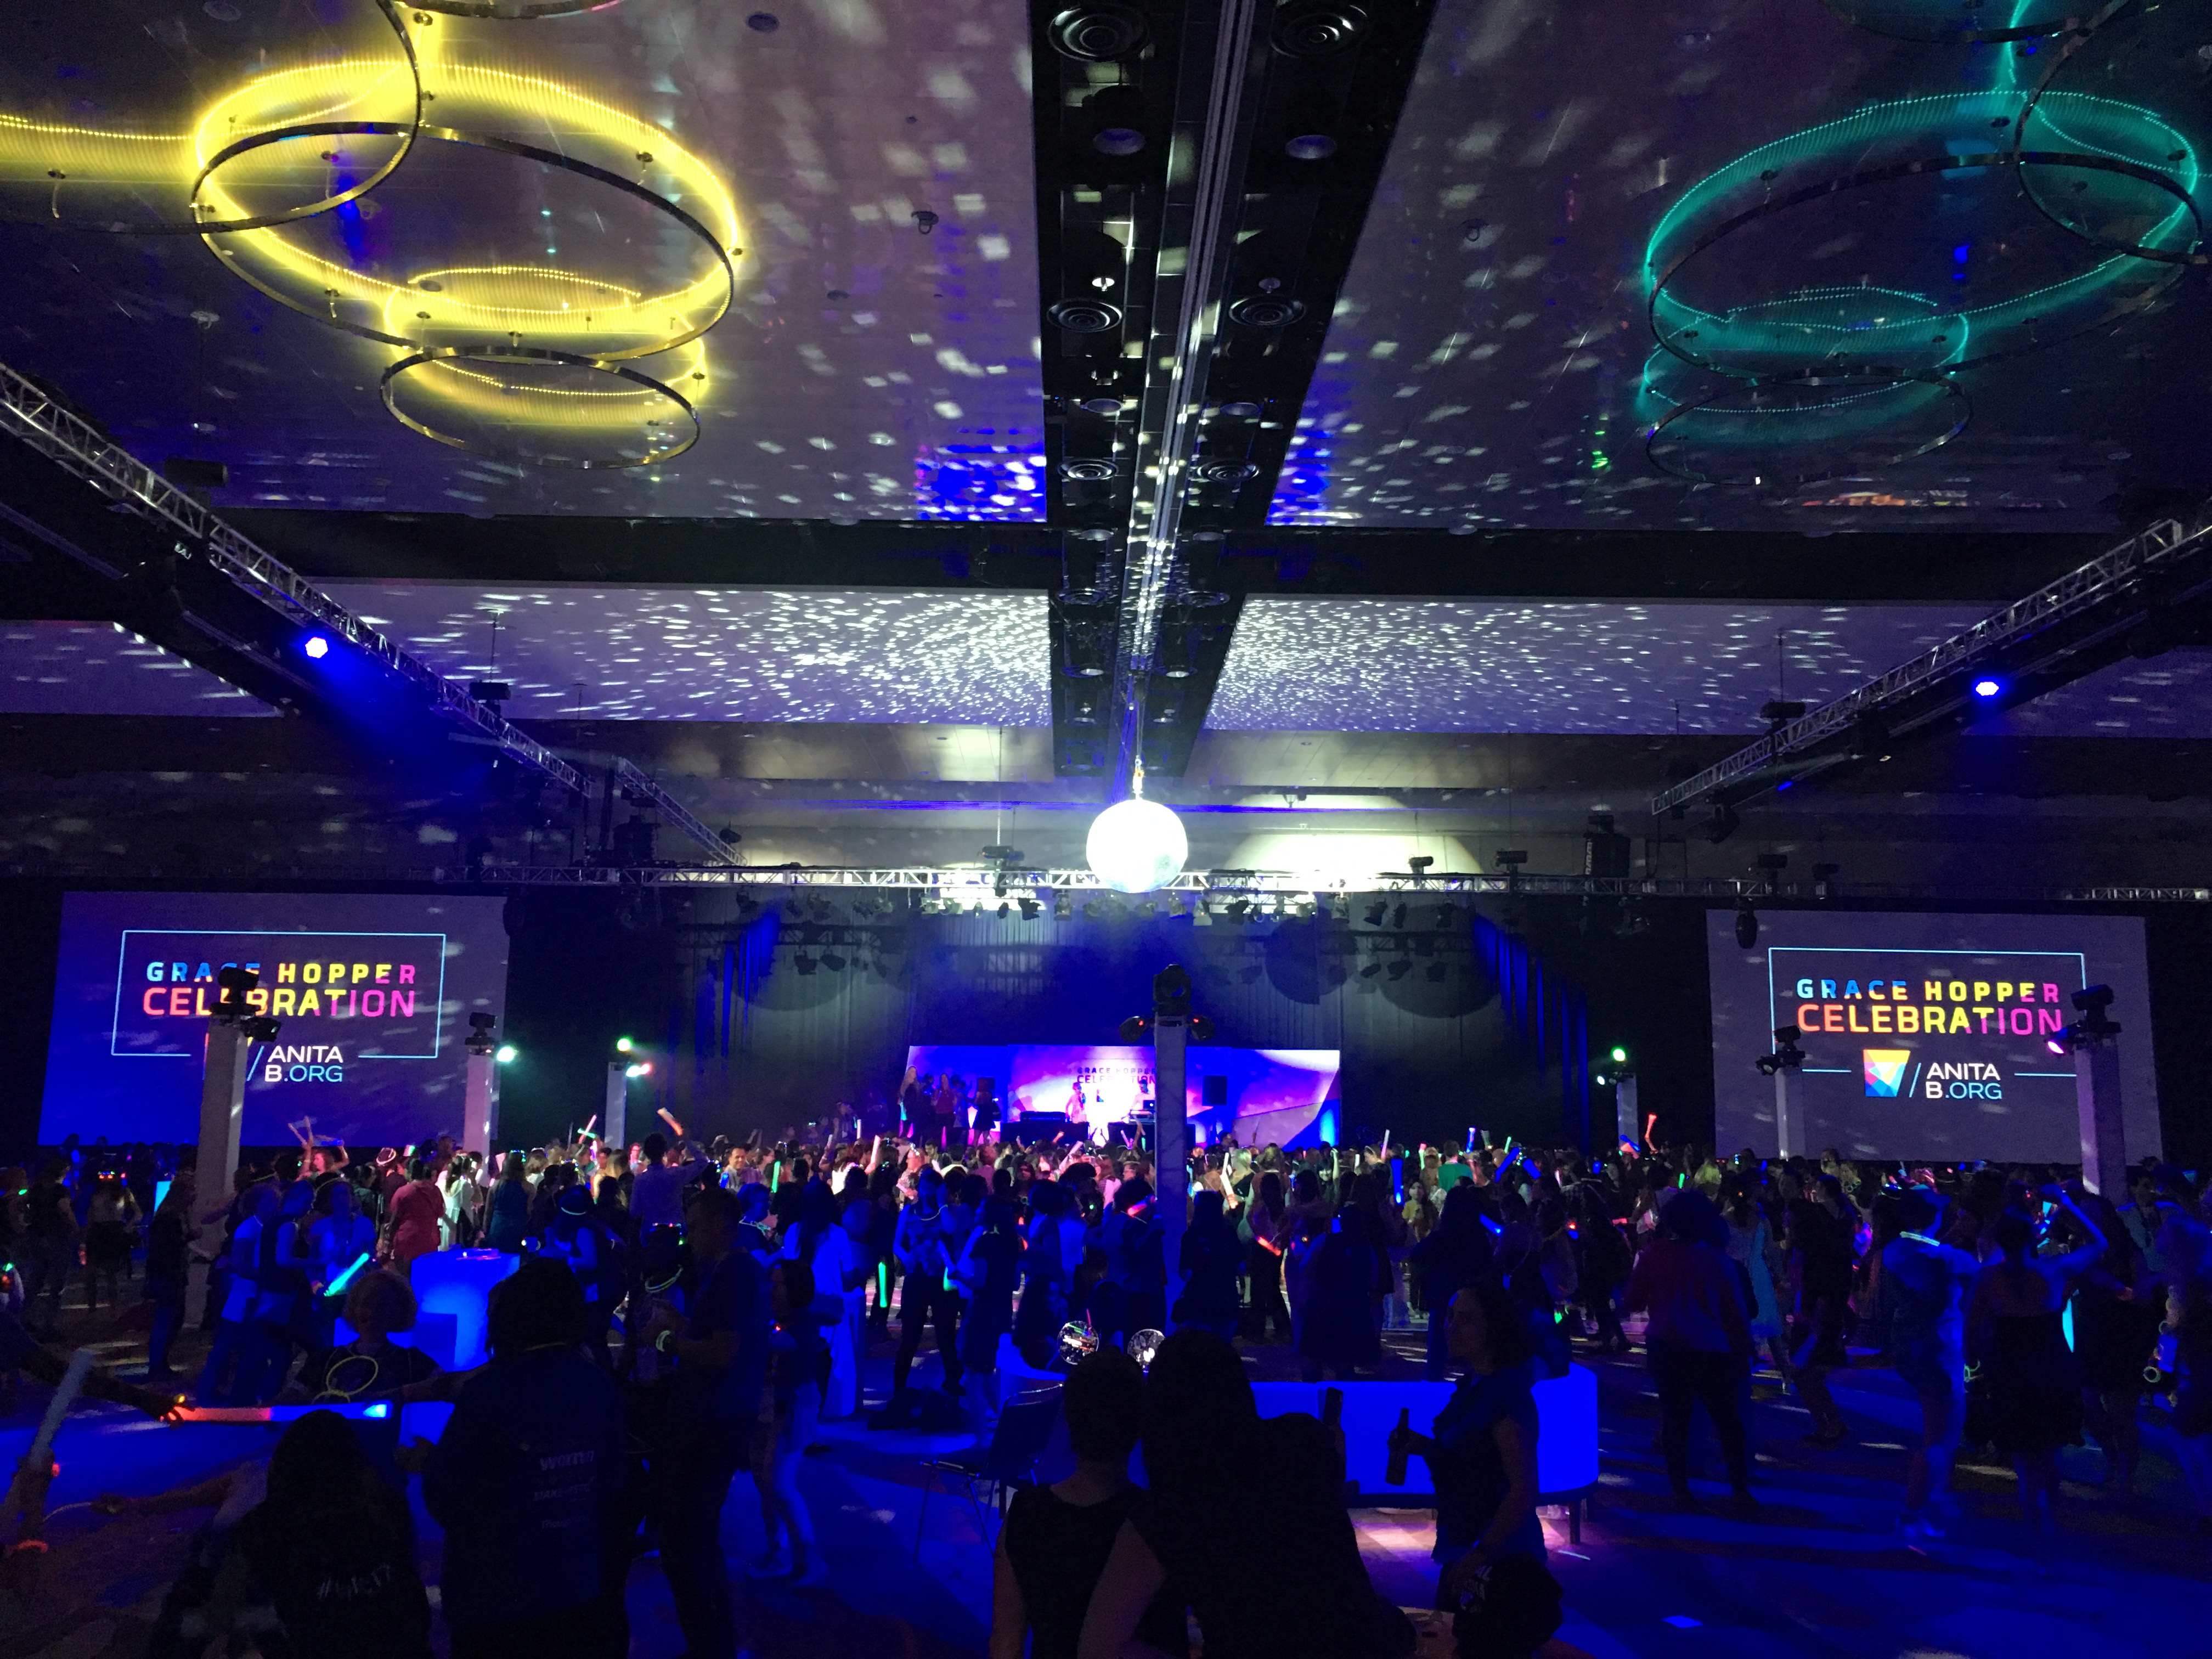 Photo by Cloudflare Staff
 Photo by Cloudflare Staff