Video: Traffic Filtering in the Age of IPv6
Christopher Werny covered another interesting IPv6 security topic in the hands-on part of IPv6 security webinar: traffic filtering in the age of dual-stack and IPv6-only networks, including filtering extension headers, filters on Internet uplinks, ICMPv6 filters, and address space filters.
Video: Traffic Filtering in the Age of IPv6
Christopher Werny covered another interesting IPv6 security topic in the hands-on part of IPv6 security webinar: traffic filtering in the age of dual-stack and IPv6-only networks, including filtering extension headers, filters on Internet uplinks, ICMPv6 filters, and address space filters.
Parsing Text using TTP
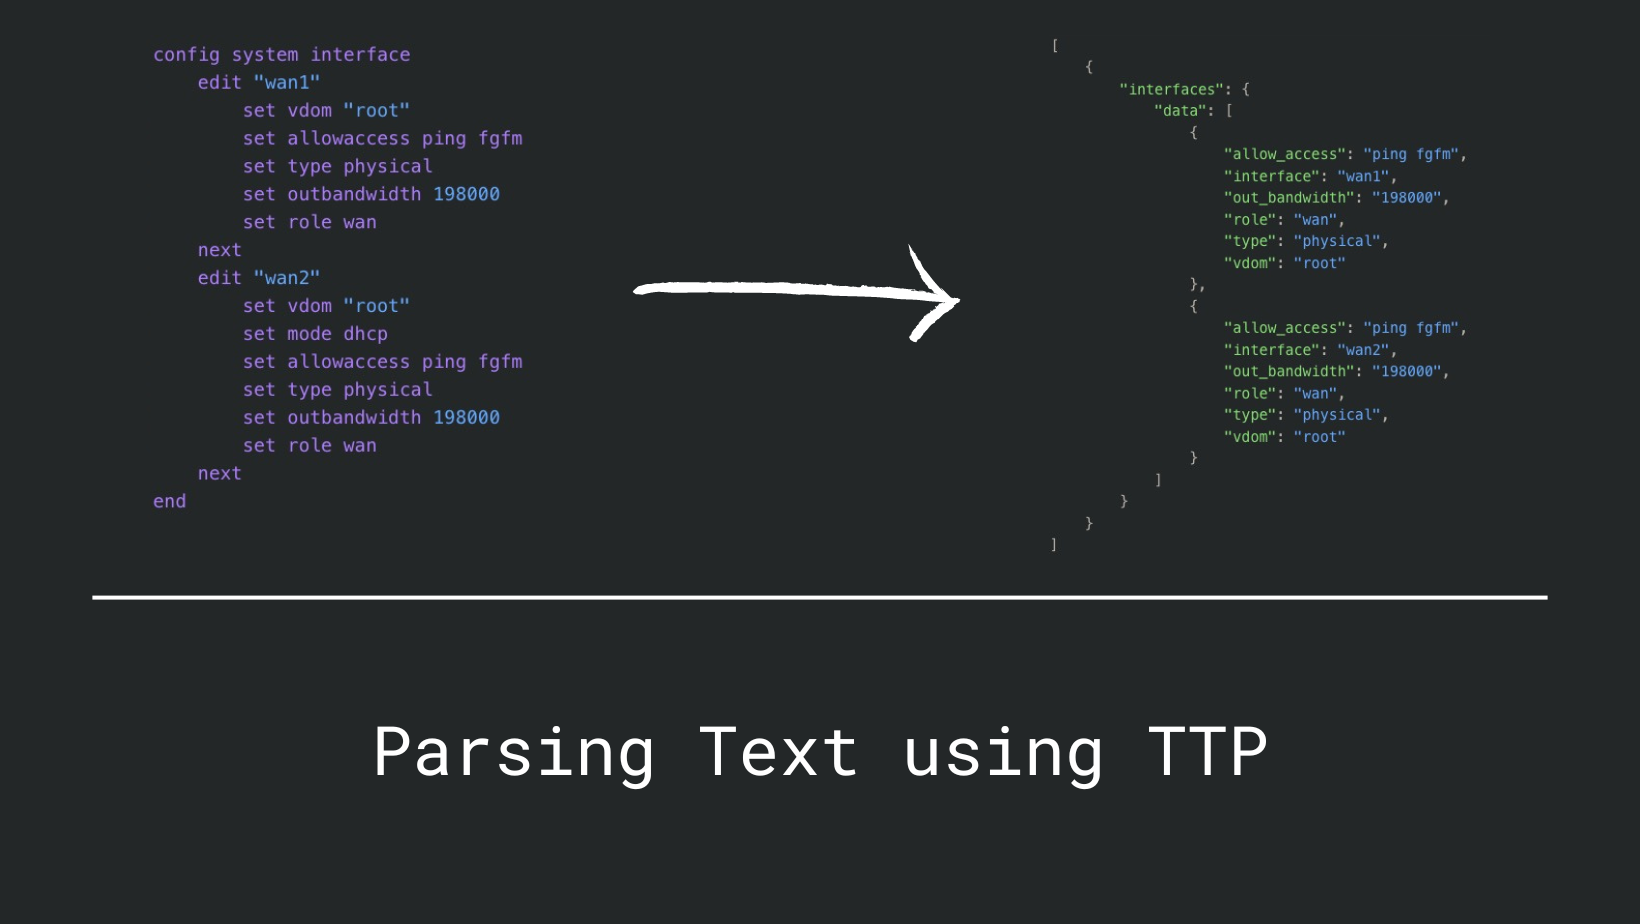
Before we dive into TTP (Template Text Parser), let us first address why we need a text scraping tool in the modern world of APIs and structured data. Here is my opinion:
- Many organisations still use legacy devices that do not have APIs or structured data formats embedded in their CLI.
- Network devices are still evolving and not all devices have APIs that are easy to work with.
- There is more information in the output of a command than what is available through the API.
- Network Engineers are used to working with CLI and screen scraping is a natural extension of this workflow.
- Sometimes you just need to get some data quickly and writing a full-fledged API client is not worth the effort.
You would be surprised to know that many commercial tools that do network observability use screen scraping under the hood. So, it is not a bad idea to learn how to do it yourself.
What are our options?
From a network engineer's perspective, there are two popular tools that can be used for screen scraping:
- TextFSM - TextFSM is a mature tool that has been around for a long time with huge community support and a large Continue reading
Walking the Policy Tightrope
In policy work nothing is ever truly simply black and white. The means to achieve one outcome may well act to impair the work to achieve different outcomes, and the resultant effort often requires some difficult decisions to balance what appears to be some fundamental tensions between various policy objectives. Even a topic like online safety, which should be very straightforward, has some challenges.Streamlining the User Experience for Accessing AKS Clusters
Lately I’ve been spending a little bit of time building Pulumi programs to assist with standing up Azure Kubernetes Service (AKS) clusters. I’ve learned a pretty fair amount about Azure and AKS along the way, as expected, but I was taken aback by the poor user experience (in my opinion) when it came to accessing the AKS clusters once they’d been established. In this post, I’ll share a small tweak you can make that will, in most cases, make accessing your AKS clusters a great deal smoother.
What do I mean by “poor user experience”? In the same vein as comparable offerings from AWS (EKS) and Google Cloud (GKE), AKS leverages Azure’s identity and access management (IAM) functionality, so that users have a single place to manage user and group entities. This makes perfect sense! What doesn’t make sense to me, though, is the requirement that users must perform a separate login process to gain access to the cluster, even if the user is already authenticated via the Azure CLI. This is very counter to both EKS and GKE, where—if you are already authenticated via their CLI tools—no additional steps are necessary to access appropriately-configured managed Kubernetes clusters on their Continue reading
Total TLS: one-click TLS for every hostname you have
Today, we’re excited to announce Total TLS — a one-click feature that will issue individual TLS certificates for every subdomain in our customer’s domains.
By default, all Cloudflare customers get a free, TLS certificate that covers the apex and wildcard (example.com, *.example.com) of their domain. Now, with Total TLS, customers can get additional coverage for all of their subdomains with just one-click! Once enabled, customers will no longer have to worry about insecure connection errors to subdomains not covered by their default TLS certificate because Total TLS will keep all the traffic bound to the subdomains encrypted.
A primer on Cloudflare’s TLS certificate offerings
Universal SSL — the “easy” option
In 2014, we announced Universal SSL — a free TLS certificate for every Cloudflare customer. Universal SSL was built to be a simple “one-size-fits-all” solution. For customers that use Cloudflare as their authoritative DNS provider, this certificate covers the apex and a wildcard e.g. example.com and *.example.com. While a Universal SSL certificate provides sufficient coverage for most, some customers have deeper subdomains like a.b.example.com for which they’d like TLS coverage. For those customers, we built Advanced Certificate Manager — a Continue reading
NTT Announces City-Wide Private 5G for Las Vegas
The private 5G network is expected to deliver ultra-low latency, more reliable connectivity, greater capacity, and robust security throughout the city.IPv6 Buzz 111: IPv6 And The Public Cloud
What's the state of IPv6 in the public cloud? What support is available in which of the major providers? What are the cloud challenges of v6? How does v6 affect multi-cloud architectures? The latest episode of the IPv6 Buzz podcast examines these and other v6 questions for public cloud.IPv6 Buzz 111: IPv6 And The Public Cloud
What's the state of IPv6 in the public cloud? What support is available in which of the major providers? What are the cloud challenges of v6? How does v6 affect multi-cloud architectures? The latest episode of the IPv6 Buzz podcast examines these and other v6 questions for public cloud.
The post IPv6 Buzz 111: IPv6 And The Public Cloud appeared first on Packet Pushers.
The Art Of System Design As HPC And AI Applications Diverge
Predicting the future is hard, even with supercomputers. And maybe specifically when you are talking about predicting the future of supercomputers. …
The Art Of System Design As HPC And AI Applications Diverge was written by Timothy Prickett Morgan at The Next Platform.
Hedge 149: Roundtable

Who’s using the cloud? Is cheap complexity harmful? Are mainframes dead? Is this the end of specialized networking hardware? Is it a good idea to have server folks build networks? On this episode of the Hedge, Tom, Eyvonne, and Russ go “guestless” in a roundtable about various topics and ideas in the networking world. Listen here—
How to Reduce Varicose Veins from a Sedentary Lifestyle
Varicose veins are a common condition that occurs when the valves in the veins become damaged and allow blood to flow backwards. This can cause the veins to become enlarged and twisted. Although varicose veins can occur at any age, they are more common in people over the age of 50 and in women who have been pregnant. People who have a sedentary lifestyle are also at increased risk for developing varicose veins. The good news is that there are several things you can do to reduce your risk of developing varicose veins.
Ways to Reduce Varicose Veins from a Sedentary Lifestyle
Exercise regularly
Doing regular physical activity helps keep the blood flowing throughout your body. Aim for 30 minutes of aerobic exercise at least five days a week. Walking, jogging and swimming are all good activities to help reduce your risk of developing varicose veins.
Wear compression stockings
Compression stockings are tight-fitting stockings that help reduce the pressure in your veins, which can help prevent varicose veins from developing. Your doctor can recommend the best type of stocking for you.
Elevate your legs
Lying down and propping your legs up above your heart can help reduce the pressure in Continue reading
More Arista EOS BGP Route Reflector Woes
Most BGP implementations I’ve worked with split the neighbor BGP configuration into two parts:
- Global configuration that creates the transport session
- Address family configuration that activates the address family across a configured transport session and changes the parameters that affect BGP updates
AS numbers, source interfaces, peer IPv4/IPv6 addresses, and passwords clearly belong to the global neighbor configuration.
More Arista EOS BGP Route Reflector Woes
Most BGP implementations I’ve worked with split the neighbor BGP configuration into two parts:
- Global configuration that creates the transport session
- Address family configuration that activates the address family across a configured transport session, and changes the parameters that affect BGP updates
AS numbers, source interfaces, peer IPv4/IPv6 addresses, and passwords clearly belong to the global neighbor configuration.
Aryaka Adds Secure Web Gateway, Firewall Service To Its SD-WAN And Security Capabilities
Aryaka is introducing both a Secure Web Gateway (SWG) and a Firewall-as-a-Service (FWaaS) offering to complement its SD-WAN capabilities. Many vendors, including Aryaka, are extending their SD-WAN offering to include security functions delivered as-a-service via Points of Presence (PoPs) or public clouds. This as-a-service approach makes it easier for customers to consume security services because […]
The post Aryaka Adds Secure Web Gateway, Firewall Service To Its SD-WAN And Security Capabilities appeared first on Packet Pushers.