TNO063: Automating Human-Centric NetOps is Finally Achievable
Scott sits down with Avi Freedman, CEO and co-founder of Kentik, to discuss if AI has advanced enough to automate human-centric NetOps. Together they caution against vendor hype regarding closed-loop network automation despite the progress AI has made. Avi also shares his personal experiences in the industry and the hard won lessons he learned along... Read more »HN828: How Selector Unifies Cloud and On-Prem Network Observability (Sponsored)
Selector is extending its AI-driven network observability capabilities into public clouds. On today’s sponsored episode, we dig into how Selector gathers and analyzes public cloud network telemetry, how it integrates cloud and on-prem network data to provide end-to-end visibility, how it integrates with third-party Application Performance Monitoring (APM) systems to correlate network and application performance,... Read more »Hedge 306: RPKI Transport
Synchronizing information across the Internet, at an initial glance, looks like a fairly simple problem to solve. Just copy a file to a host and create a magic protocol, right? Not really. Each kind of data has a fairly unique set of requirements–and RPKI data, used to provide security information for BGP, is no different. Job Snijders joins Tom and Russ to talk about ERIK, a protocol developed to synchronize RPKI records.
For more information, check out Job’s web site and the IETF draft.
download
Public Videos: OpenFlow Deep Dive
Remember OpenFlow, the One Protocol to Bind Them All1? I haven’t heard anyone even mention it in ages, and I never bothered to ask whether anyone is still using it after the dismal results of the 2022 poll.
Anyway, if you still have to deal with that ancient blunder, six hours of deep dive videos I recorded a decade ago might still be useful. You can watch them without an ipSpace.net account.
Looking for more binge-watching materials? You’ll find them here.
Announcing Claude Compliance API support with Cloudflare CASB
Today, we are extending Cloudflare’s cloud access security broker (CASB) to support the Claude Compliance API. Security and compliance teams can now monitor Claude usage directly in the Cloudflare dashboard. No endpoint agents required.
Enterprise security teams have long struggled to see how users interact with sanctioned and unsanctioned applications. The rapid adoption of AI applications has made this harder. Employees spend significant time in these new surface areas, and their interactions differ from traditional SaaS: users upload files, share freeform prompts, and providers generate content that may contain sensitive data.
Cloudflare CASB helps solve this problem. One API integration gives you out-of-band visibility and control over the applications your organization uses. This integration builds on our existing support for AI governance, extending coverage over the most common tools security teams now manage.
AI adoption has outpaced security governance. While IT and security teams raced to enable AI tools for productivity, the controls lagged behind. Most organizations today operate with partial visibility: they may block unauthorized AI tools at the network layer, but they cannot see what happens inside sanctioned ones.
This matters because AI tools are not like traditional SaaS Continue reading
LIU015: Eyvonne Sharp: From Farm Roots to the Cloud
Today’s guest is Eyvonne Sharp, a Google Cloud technical leader, Network Collective co-founder, co-host of The Cloud Gambit podcast, and former network architect at a Fortune 100. Eyvonne shares stories from her impressive career, offers advice to her younger self, and how to appreciate those “magic” moments in your career when a project fires on... Read more »Dual-Stack SR-MPLS
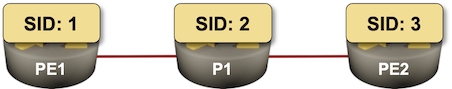
After the introduction to SR-MPLS demo I did during the Segment Routing workshop @ ITNOG10, we moved to dual-stack SR-MPLS – can we assign node segment identifiers (SIDs) to IPv4 and IPv6 prefixes? The demo used the same three-router network as the previous one, with IPv4 SIDs starting at one and IPv6 SIDs starting at 101:
Cisco Launches Major Updates to Certifications
Cisco just announced major updates to their certification portfolio. Here’s what’s changing:
- CCNA v2.0
- CCIE practical exam AI DOO module
- CCIE automation v1.2
CCNA v2.0
Effective February 2027, the CCNA is getting a major update. The future networking administrator/engineer will be more of an orchestrator than operator. Meaning that punching commands on the CLI will only be a small part of the future job role. Instead, you must be able to design, secure, and optimize increasingly autonomous networks. To be job-ready, you’ll need to learn how to:
- Troubleshoot production issues under pressure
- Evaluate what an AI assistant recommends and know when it’s wrong
- Secure an environment by design, not an afterthought
The CCNA is about to get a whole lot more practical! Here’s what’s changing:
Troubleshooting gets a front seat. Employers value troubleshooting over reciting commands. Every domain will diagnostics and problem resolution. Think of the old TSHOOT CCNP exam, but instead of a separate exam, this is the format of the CCNA now. I’m really excited about this!
Security everywhere. We can no longer afford to think of security only as a separate domain, it needs to be part of everything we do. The new exam Continue reading
BGP and Multi-Cloud Routing
 For years, enterprise cloud networking was built around a simple assumption: pick a primary cloud provider, connect the data center to it, and expand from there.
That model no longer reflects how many organizations actually operate.
Today, workloads often live across AWS, Azure, and Google Cloud at the same time. Sometimes this is intentional. Sometimes it is the result of acquisitions, separate engineering teams, SaaS dependencies, regional requirements, or SaaS platforms that depend on a specific cloud provider. Either way, the network has to make these environments behave like one reliable system.
That is where the hard part begins.
Cloud-native routing tools are useful inside each provider, but they do not automatically solve routing between providers, between clouds and colocation hubs, or between multiple cloud environments and an enterprise WAN. Once routing needs to become dynamic, policy-driven, and resilient across administrative boundaries, BGP becomes the common language.
BGP is not new, and it is not always simple. But in multi-cloud networking, it remains one of the few mechanisms that AWS, Azure, Google Cloud, carriers, colocation providers, SD-WAN platforms, and enterprise routers can all understand.
What inter-cloud routing actually means
The term “inter-cloud routing” is often used loosely, so it is Continue reading
NAN123: How ION Meets the Out-of-this-World Challenges of Deep-Space Networking
Eric Chou and guest host Drew Conry-Murray sit down with deep space networking specialist Scott Spicer. Following the Artemis 2 mission, they discuss the challenges of long-delay space communications and the essential technologies making it possible such as the Interplanetary Overlay Network (ION), Delay-Tolerant Networking (DTN), and Contact Graph Routing (CGR). AdSpot Sponsor: Meter Meter... Read more »TCG076: Packet Pushers Assemble! Bridging the Telemetry Divide
Today our Packet Pushers team assembles to discuss whether the grass is greener on the NetOps or DevOps side of the telemetry fence. William of The Cloud Gambit, Scott of Total Network Operations, and Ned and Kyler of Day Two DevOps discuss the difficulties and differences of getting telemetry and state from devices across different... Read more »My Network is Talking Back Thanks to SuzieQ MCP and it’s Channeling Sam Kinison
Last Updated: 2025-05-19 Every SuzieQ Enterprise release quietly adds things that end up being genuinely useful in day-to-day network operations. Version 3.3 has had a few updates already. The GUI has seen a lot of attention. The new workbench makes it even easier to get at your data without jumping around, and you can now READ MORE
The post My Network is Talking Back Thanks to SuzieQ MCP and it’s Channeling Sam Kinison appeared first on The Gratuitous Arp.
Worth Reading: Agentic AI Setup: Sandboxes and Worktrees
Most of the hyperventilated AI “success stories” are as useful as the “ANSIBLE!!!” movement was a few years ago. It’s thus always a pleasure to find someone with well-established software development chops who took the time to describe what works for them.
One cannot argue with Mike McQuaid’s credentials (at least if you happen to be using homebrew on MacOS, which you REALLY SHOULD), and his Sandboxes and Worktrees: My secure Agentic AI Setup in 2026 article is full of relevant recommendations in case you’re brave enough to let AI agents loose on your GitHub repository.
Encrypted DNS at OARC 46
Much has been said about the use of the DNS as a means of tracking and controlling the online behaviour of users. The response has been to hide the DNS behind encrypted transport.Encrypted DNS at OARC 46
Much has been said about the use of the DNS as a means of tracking and controlling the online behaviour of users. The response has been to hide the DNS behind encrypted transport.phpIPAM installation on Ubuntu Server 26.04 LTS
How to install phpipam on Ubuntu Server 26.04 LTS server.PP110: News Roundup–Linux Fragged, Edge’s Password Manager Dragged, Android Intrusions Tagged, and More
JJ and Drew unpack an overstuffed suitcase of infosec stories in today’s News Roundup. Microsoft’s Edge password manager stores credentials in plaintext and Microsoft says “Yup”, the Linux kernel takes a one-two punch from Dirty Frag and Fragnesia, and a new industry coalition takes critical infrastructure protection private. A Taiwanese radio enthusiast allegedly brings high-speed... Read more »HS132: Heart of Glasswing
How can enterprise IT folks prepare for the age of Mythos? Anthropic says its Claude Mythos model is so much better at finding software vulnerabilities that it has delayed public release. Instead Anthropic launched Project Glasswing to give IT infrastructure and software makers early access, so they can have some lead time to address vulnerabilities... Read more »