How Did We End with 1500-byte MTU?
A subscriber sent me this intriguing question:
Is it not theoretically possible for Ethernet frames to be 64k long if ASIC vendors simply bothered or decided to design/make chipsets that supported it? How did we end up in the 1.5k neighborhood? In whose best interest did this happen?
Remember that Ethernet started as a shared-cable 10 Mbps technology. Transmitting a 64k frame on that technology would take approximately 50 msec (or as long as getting from East Coast to West Coast). Also, Ethernet had no tight media access control like Token Ring, so it would be possible for a single host to transmit multiple frames without anyone else getting airtime, resulting in unacceptable delays.
Read more ...“I was told to buy a software or lose my computer: I ignored it.” A study of ransomware
“I was told to buy a software or lose my computer. I ignored it”: a study of ransomware Simoiu et al., SOUPS 2019
This is a very easy to digest paper shedding light on the prevalence of ransomware and the characteristics of those most likely to be vulnerable to it. The data comes from a survey of 1,180 US adults conducted by YouGov, an online global market research firm. YouGov works hard to ensure respondent participation representative of (in this case) the general population in the U.S., but the normal caveats apply.
We define ransomware as the class of malware that attempts to defraud users by restricting access to the user’s computer or data, typically by locking the computer or encrypting data. There are thousands of different ransomware strains in existence today, varying in design and sophistication.
The survey takes just under 10 minutes to complete, and goes to some lengths to ensure that self-reporting victims really were victims of ransomware (and not some other computer problem).

For respondents that indicated they had suffered from a ransomware attack, data was collected on month and year, the name of the ransomware variant, the ransom demanded, the payment method, Continue reading
Kubernetes, Ransomware to Hit Cloud and Data in 2020
Ransomware attacks shot up 500% in the last year with damage costs expected to soar up to $11...
Tech Bytes: Implementing Sensible Network Segmentation With Tufin (Sponsored)
Today's Tech Bytes podcast looks at how to implement sensible network segmentation to ensure compliance with security policies and accelerate business agility. Tufin is our sponsor, and we speak with guest Sagi Bar-Zvi, Strategic Pre-Sales Manager at Tufin.Tech Bytes: Implementing Sensible Network Segmentation With Tufin (Sponsored)
Today's Tech Bytes podcast looks at how to implement sensible network segmentation to ensure compliance with security policies and accelerate business agility. Tufin is our sponsor, and we speak with guest Sagi Bar-Zvi, Strategic Pre-Sales Manager at Tufin.
The post Tech Bytes: Implementing Sensible Network Segmentation With Tufin (Sponsored) appeared first on Packet Pushers.


Heavy Networking 478: Leveraging LTE For SD-WAN With Cradlepoint (Sponsored)
Today's Heavy Networking show is sponsored by Cradlepoint, which provides wireless WAN networking. Our guest Marc Bresniker, VP of Product Management, joins us to discuss using LTE for WAN connections including IoT, and to explore the benefits of using Cradlepoint's LTE solutions as part of your SD-WAN strategy.
The post Heavy Networking 478: Leveraging LTE For SD-WAN With Cradlepoint (Sponsored) appeared first on Packet Pushers.


Network Break 256: Startup Forward Networks Nabs $35 Million; Vodafone Dials OpenRAN For Incumbent Alternatives
Today's Network Break podcast is chock full of inspirational cynicism. We cover fresh funding for Forward Networks, Vodafone trialing OpenRAN gear, SUSE closing the door on OpenStack, Extreme Networks shifting StackStorm to the Linux Foundation, and more tech news.Network Break 256: Startup Forward Networks Nabs $35 Million; Vodafone Dials OpenRAN For Incumbent Alternatives
Today's Network Break podcast is chock full of inspirational cynicism. We cover fresh funding for Forward Networks, Vodafone trialing OpenRAN gear, SUSE closing the door on OpenStack, Extreme Networks shifting StackStorm to the Linux Foundation, and more tech news.
The post Network Break 256: Startup Forward Networks Nabs $35 Million; Vodafone Dials OpenRAN For Incumbent Alternatives appeared first on Packet Pushers.


PCI-Express Steps Up To The Bandwidth Challenge
Moore’s Law might be slowing down CPU compute capacity increases in recent years, but the innovation has been coming at a steady drumbeat for the interconnects used inside servers and between nodes in distributed computing systems. …
PCI-Express Steps Up To The Bandwidth Challenge was written by Timothy Prickett Morgan at The Next Platform.
Forcepoint Web Security Footprint Spans 160 Global PoPs
The vendor rolled out its Web Security platform across 160 points of presence as it builds out a...
Toshiba Taps Cybera’s SD-WAN for Retail Terminals
Under the agreement, Cybera becomes Toshiba's preferred SD-WAN vendor in the Asia-Pacific...
Intel Snaps Up Smart Edge Amid 5G Push
The company is expanding into edge computing, which it estimates will be a $65 billion silicon...
Sponsored Post: Fauna, Sisu, Educative, PA File Sight, Etleap, PerfOps, Triplebyte, Stream

Who's Hiring?
- Sisu Data is looking for machine learning engineers who are eager to deliver their features end-to-end, from Jupyter notebook to production, and provide actionable insights to businesses based on their first-party, streaming, and structured relational data. Apply here.
- Triplebyte lets exceptional software engineers skip screening steps at hundreds of top tech companies like Apple, Dropbox, Mixpanel, and Instacart. Make your job search O(1), not O(n). Apply here.
- Need excellent people? Advertise your job here!
Cool Products and Services
- Stateful JavaScript Apps. Effortlessly add state to your Javascript apps with FaunaDB. Generous free tier. Try now!
- Grokking the System Design Interview is a popular course on Educative.io (taken by 20,000+ people) that's widely considered the best System Design interview resource on the Internet. It goes deep into real-world examples, offering detailed explanations and useful pointers on how to improve your approach. There's also a no questions asked 30-day return policy. Try a free preview today.
- PA File Sight - Actively protect servers from ransomware, audit file access to see who is deleting files, reading files or moving files, and detect file copy activity from the server. Historical audit reports Continue reading
Lenovo’s Charles Ferland Shares What’s in Store for SDN, NFV, and Telecoms
Hear from Lenovo's Charles Ferland as he dives into the company's latest ideas in telecom...
Overcoming the Barriers to Micro-segmentation
It should come as no surprise how much emphasis organizations place on security today. Threats are becoming more and more sophisticated and the number of threats grow to uncontrollable rates every day.
One of the biggest downsides is that the rising cost of data breaches in 2019 alone, a global average of $3.92 million as reported by the Ponemon Institute and IBM Security July 2019 report, is enough to cause organizations to rethink or increase emphasis on their security strategies and how they can help secure their most important assets by improving the cyber hygiene in their organizations.
What is Cyber Hygiene?
Cyber hygiene refers to what an organization can do to improve their security postures around physical hardware, software, and applications. If you’ve seen Pat Gelsinger’s keynote from 2017, he goes into the 5 pillars of good cyber hygiene and what organizations can do to improve basic and fundamental security for their business.
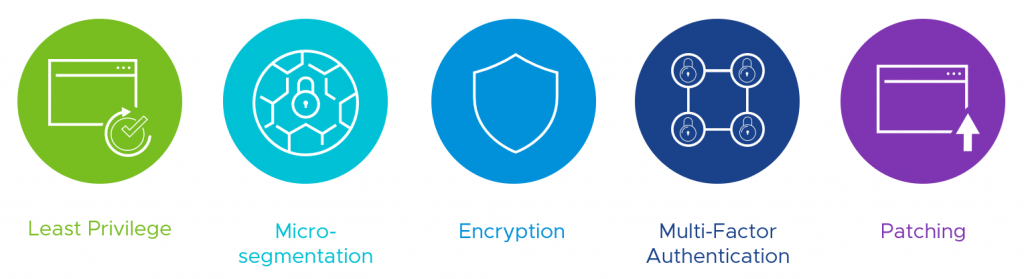
Over the last several years, VMware has been focusing on helping organizations move to Software-Defined Data Centers (SDDC) to improve their agility and meet the speed of business. As more organizations adopted the SDDC model, VMware found itself in a unique position Continue reading