Introducing Advanced Rate Limiting
Still relying solely on IP firewalling? It’s time to change that.
While the IP address might still be one of the core technologies allowing networks to function, its value for security is long gone. IPs are rarely static; nowadays, mobile operators use carrier-grade network address translation (CGNAT) to share the same IP amongst thousands of individual devices or users. Bots then carry out distributed attacks with low request volume from different IPs to elude throttling. Furthermore, many countries consider IP addresses to be personal data, and it would be a great advancement for privacy if a replacement could be found for elements of security that currently rely on IP addresses to function. A product that is affected by this trend is rate limiting.
Rate limiting is designed to stop requests from overloading a server. It relies on rules. A rate limiting rule is defined by a filter (which typically is a path, like /login) and the maximum number of requests allowed from each user over a period of time. When this threshold is exceeded, an action is triggered (usually a block) for subsequent requests from the same user for a period of time (known as a timeout). Traditional throttling Continue reading
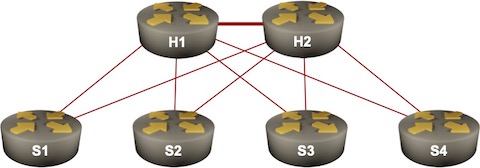



 addresses these challenges with a holistic approach to cloud networking including both the switching fabric and the compute virtualization fabric. I then explain how the Pluribus Netvisor® ONE network operating system (OS) integrates with the NVIDIA® Bluefield® data processing unit (DPU) hardware architecture to deliver a Unified Cloud Fabric across any workload environment (including ESXi, Hyper-V, Xen, KVM, bare metal, and Kubernetes), provide a zero-trust administration model between compute and network, and radically simplify the networking stack running on the server OS with better overall performance and lower TCO. Finally, I review the initial set of use cases Pluribus is delivering with the Early Field Trial (EFT) program starting next month.