Meet NFA v26.02, featuring BGP visibility tools, extended threshold matching, and SNMP reporting enhancements.
We’re excited to announce the release of Noction Flow Analyzer v26.02. This version includes a focused set of improvements that enhance BGP visibility, expand threshold-monitoring options, improve flow-processing performance, and refine the SNMP reporting experience. This update builds on the foundation of v26.01 and introduces new tools for network engineers who rely on real-time routing intelligence and traffic analysis.
BGP diagnostics and visibility tools
The biggest addition in v26.02 is a complete set of BGP diagnostics and visibility tools. These give network administrators new insights into routing behavior directly within NFA. The new BGP diagnostics panel introduces ping and traceroute checks, allowing engineers to run connectivity and path diagnostics without leaving the NFA interface. Additionally, a BGP Data Lookup feature enables direct queries against NFA’s internal BGP tables, supporting exact-match and more-specific match modes for precise prefix investigations. Finally, BGP History Lookup provides access to historical route events, including key attributes such as prefix, next-hop, AS path, and more. This makes it easier to trace routing changes over time and connect them with traffic events.
We’re excited to announce the release of Noction Flow Analyzer v26.02. This version includes a focused set of improvements that enhance Continue reading
Pytest for Automated Network Testing (II)
In part one, we covered the basics of pytest and wrote our first network tests. We tested BGP and OSPF on a single device, then extended it to multiple devices. We also looked at parametrization and how it helps treat each device and each neighbour as an independent test.
In this part, we will cover inventory management with Nornir and pytest fixtures.
Pytest for Automated Network Testing
Pytest gives you full control. You write the test, you decide exactly what to check, and you get a clear pass or fail result. You can test one device
 Suresh Vinasiththamby
Nornir Introduction
Nornir is a Python automation framework designed for network engineers. Instead of writing your own logic to connect to devices, manage inventory, and run tasks in parallel, Nornir handles all of that for you. We have a dedicated series on Nornir, which you can check out here, so we are not going to do a deep dive in this post.
The reason we are using Nornir here is for inventory and task management. Instead of hardcoding a list of IP addresses in our collection file, we define our devices in a hosts file with groups, credentials, and Continue reading
PP109: ThreatLocker Enforces Zero Trust With Strict Application Control (Sponsored)
ThreatLocker takes an opinionated approach to Zero Trust. The company, our sponsor for today’s episode, starts with application control. It uses endpoint software that runs on PCs and servers to allow or deny applications to run. It can also monitor and control the behavior of allowed applications. ThreatLocker has extended its platform to include network... Read more »HW078: Companion Tools for Wireless Validation Surveys
Guest Nick Turner joins Keith to discuss the technicalities of Wi-Fi validation survey file structures. Nick has spent a lot of time deep in the weeds of .ESX files, and he’s here to share workflows and utilities you can use to help navigate, migrate, back up, and operationalize .ESX files. If you’ve ever wondered exactly... Read more »When “idle” isn’t idle: how a Linux kernel optimization became a QUIC bug
CUBIC, standardized in RFC 9438, is the default congestion controller in Linux, and as a result governs how most TCP and QUIC connections on the public Internet probe for available bandwidth, back off when they detect loss, and recover afterward. At Cloudflare, our open-source implementation of QUIC, quiche, uses CUBIC as its default congestion controller, meaning this code is in the critical path for a significant share of the traffic we serve.
In this post, we’ll tell the story of a bug in which CUBIC's congestion window (cwnd) gets permanently pinned at its minimum and never recovers from a congestion collapse event.
The story starts with a Linux kernel change aimed at bringing CUBIC into line with the app-limited exclusion described in RFC 9438 §4.2-12 — a fix to a real problem in TCP that, when ported to our QUIC implementation, surfaced unexpected behaviors in quiche. It has a happy ending: an elegant (near-)one-line fix that broke the cycle.
Before we dive into the core problem, a quick refresher on Congestion Control Algorithms (CCAs) may help to set the stage.
The central knob a CCA turns is the congestion window (cwnd Continue reading
MUST READ: The Future of Everything is Lies, I Guess
Kyle Kingsbury published a long (10-part) article about his frustrations with AI, aptly named The Future of Everything is Lies, I Guess.
Regardless of where you are on the skeptic-to-fanboy spectrum, I would highly recommend you read it, even if you believe you’ll disagree with everything he wrote.
NB574: Extreme’s New AI Agent Nudges You; Cloudflare Evaporates 20% of Employees
Take a Network Break! There’s a Red Alert for Apache Polaris with four CVEs that could enable unauthorized read/write access. On the news front, Lumen is spending $475 million in cash for Alkira to extend its NaaS offering across public clouds. Extreme Networks announces Wi-Fi 7 APs and new features in its Platform ONE management... Read more »Understanding Scale-Out, Scale-Up, and Scale-Across Networking
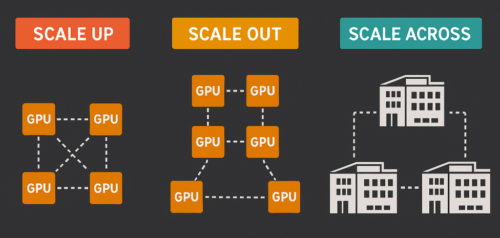
Modern AI and HPC workloads place extraordinary demands on the underlying network infrastructure. And as network engineers, we are often pulled into conversations about GPU clusters, maybe without a clear…
The post Understanding Scale-Out, Scale-Up, and Scale-Across Networking appeared first on JTnetwork.io.
Reorganized ipSpace.net Segment Routing Resources
I created nine sample SR-MPLS topologies for the ITNOG 10 SR-MPLS workshop, and of course, we ran out of time. I plan to cover those topologies and resulting printouts in a series of blog posts; to prepare for those, I cleaned up and reorganized the Segment Routing blog category, which is now split into two:
Hope you’ll find them useful! Also, if you know of other non-vendor Segment Routing resources, please leave a comment, email me, or submit a pull request.
Quantum safe amateur radio secure shell
I’ve previously pointed out that the AX.25 implementation in the kernel is pretty poor. It’s not really being maintained, and even when it gets fixes after I reported it, with people running LTS OSs it can take like 5 years before before the fix actually reaches users, if ever. So when writing applications, you still have to work around kernel bugs from a decade ago. This makes it kind of pointless to upstream patches.
The exception is security patches, and reading between the lines of why the AX.25 code is now being removed from the kernel, it sounds like maybe some LLM (like the looming “Mythos” and the related Glasswing) may have found some severe problems. But even if there aren’t any known security problems yet, having code is now more of a liability than ever. Code needs to be removed, or taken responsibility of. (tangent about ffmpeg at the bottom of this post)
With the kernel code removed, say goodbye to the old walkthrough.
The new API
Well, not “new”, per se, but “replacement”.
With the socket based API about to be gone, we need some other way for applications to send packets and Continue reading
phpIPAM version 1.8 released
New version of phpipam (1.8) released.TNO062: SONiC for Open Networking with Jeff Doyle
Scott Robohn is joined by networking legend Jeff Doyle to help us understand SONiC: Software for Open Networking in the Cloud. SONiC is an open-source network operating system and has been adopted by hyperscalers to run some of the world’s largest data centers. But SONiC can also be used by enterprises and service providers. Jeff... Read more »HN826: An Inside Look at Palo Alto Networks Prisma Browser for Business (Sponsored)
A Mastercard survey reveals that 46% of small and medium businesses have experienced a cyberattack, and nearly 20% of those that suffered an attack were then forced to file for bankruptcy or close their business. Ethan and Drew along with guest Shivam Srivastava discuss a new offering from today’s sponsor, Palo Alto Networks: Prisma Browser... Read more »SecureCRT to SuperPutty – Migrate Your Sessions with One Python Script
If you’ve ever had to move a large session library from SecureCRT to SuperPutty, you know the pain — there’s no built-in migration path, and manually re-entering dozens (or hundreds) of sessions is a miserable afternoon. I wrote SCRT_2_SPUTTY to handle it automatically. Point it at your SecureCRT XML export, and it spits out a...
The post SecureCRT to SuperPutty – Migrate Your Sessions with One Python Script first appeared on Fryguy's Blog.SecureCRT to SuperPutty – Migrate Your Sessions with One Python Script
If you’ve ever had to move a large session library from SecureCRT to SuperPutty, you know the pain — there’s no built-in migration path, and manually re-entering dozens (or hundreds) of sessions is a miserable afternoon. I wrote SCRT_2_SPUTTY to handle it automatically. Point it at your SecureCRT XML export, and it spits out a ready-to-import SuperPutty XML file. No third-party libraries, no configuration files — just Python and a single command.
Hedge 304: Deep Dive into a Network Master’s Program
If you’ve ever been curious about what an advanced degree in network engineering looks like, you’ll want to join us for this episode of the Hedge. Levi Perigo from the University of Colorado at Boulder joins Tom and Russ to talk through what earning a Master’s in Networking involves and what kinds of things you would learn.
download
Public Videos: Segment Routing 101
In the spring of 2017, Jeff Tantsura, the IETF Routing Area chair, delivered a short “Introduction to Segment Routing” webinar. In mid-April 2026, we had ~100 people at ITNOG 10 attending the excellent “Segment Routing: From Theory to Practice” workshop by the great Tiziano Tofoni. The future is obviously not evenly distributed.
If you’re in the early stages of your Segment Routing journey, you might appreciate the videos from Jeff’s webinar; you can now watch them without an ipSpace.net account.
Building for the future
This afternoon, we sent the following email to our global team. One of our core values at Cloudflare is transparency, and we believe it's important that you hear this directly from us because it’s a major moment at Cloudflare.
Team:
We are writing to let you know directly that we’ve made the decision to reduce Cloudflare’s workforce by more than 1,100 employees globally.
The way we work at Cloudflare has fundamentally changed. We don’t just build and sell AI tools and platforms. We are our own most demanding customer. Cloudflare’s usage of AI has increased by more than 600% in the last three months alone. Employees across the company from engineering to HR to finance to marketing run thousands of AI agent sessions each day to get their work done. That means we have to be intentional in how we architect our company for the agentic AI era in order to supercharge the value we deliver to our customers and to honor our mission to help build a better Internet for everyone, everywhere.
Today is a hard day. This decision unfortunately means saying goodbye to teammates who have contributed meaningfully to our mission and to building Cloudflare Continue reading