We are excited to introduce the early preview releases for Calico Enterprise 3.17. This release focuses on helping enterprises have a strong security posture for their containers and Kubernetes clusters. Let’s go through some of the highlights of this release.
Namespace isolation with automatic Security Policy Recommendations
Calico will now automatically generate security policies based on workload dependencies and incoming and outgoing traffic to isolate namespaces in your Kubernetes cluster.
WireGuard support for AKS and EKS with Calico CNI
Users can now protect data-in-transit data in Microsoft AKS and Amazon EKS clusters by enabling WireGuard encryption with the Calico CNI.
Improved management of Workload-based WAF
Secure specific workload-to-workload communications at the application level with Calico’s workload-based web application firewall (WAF) by selecting and deselecting specific services.
Policy-based routing for egress gateways
Define policies on which egress gateway to use (or none at all) depending on the destination of egress traffic.
We hope you’ll enjoy these product upgrades and enhancements. We will continue to deliver new releases with innovative solutions to solve container and Kubernetes security challenges. Watch this space for future updates and details about how to leverage these features in your environment.
Check out our self-paced workshops for Continue reading
The debates around IP multicast stopped about five to ten years ago AFAICT. No one wants to deal with it anymore. In theory, IP multicast was a good idea but in the real world it was a deeply flawed.
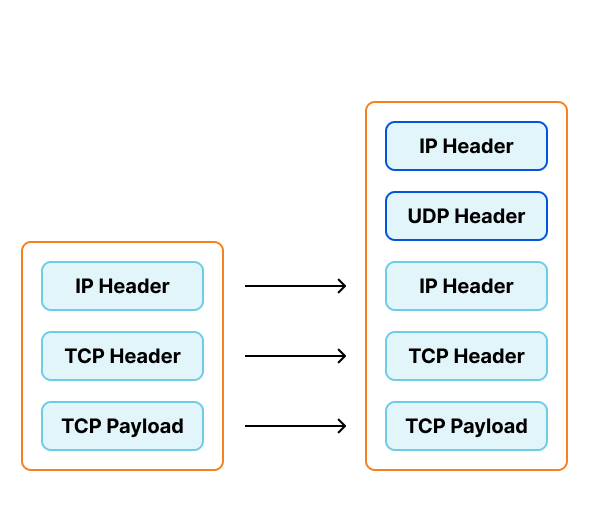
Previously, I wrote about building network load balancers with the maglev scheduler, which we use for ingress into our Kubernetes clusters. At the time of that post we were using Foo-over-UDP encapsulation with virtual interfaces, one for each Internet Protocol version for each worker node.
To reduce operational toil managing the traffic director nodes, we've recently switched to using IP Virtual Server's (IPVS) native support for encapsulation. Much to our surprise, instead of a smooth change, we instead observed significant drops in bandwidth and failing API requests. In this post I'll discuss the impact observed, the multi-week search for the root cause, and the ultimate fix.
To support our requirements we've been creating virtual interfaces on our traffic directors configured to encapsulate traffic with Foo-Over-UDP (FOU). In this encapsulation new UDP and IP headers are added to the original packet. When the worker node receives this packet, the kernel removes the outer headers and injects the inner packet back into the network stack. Each virtual interface would be assigned a private IP, which would be configured to send traffic to these private IPs in "direct" mode.

This configuration presents several problems for our operations teams.

This post is also available in Deutsch.

Speed Week 2023 is officially a wrap.
In our Welcome to Speed Week 2023 blog post, we set a clear goal:
“This week we will help you measure what matters. We’ll help you gain insight into your performance, from Zero Trust and API’s to websites and applications. And finally we’ll help you get faster. Quickly.”.
This week we published five posts on how to measure performance, explaining which metrics and approaches make sense and why. We had a deep dive on the latest Core Web Vital, “Interaction to Next Paint”, what it means and how we can help. There was a post on Time To First Byte (TTFB) and why it isn't a good way to measure good web performance. We also wrote about how to measure Zero Trust performance, and announced the Internet Quality page of Cloudflare Radar - giving everyone the ability to compare Internet connection quality across Internet Service Providers, countries, and more.
We launched new products such as Observatory, Digital Experiencing Monitoring and Timing Insights. These products give an incredible window into how your applications and websites are performing through the eyes of website visitors Continue reading
This blog is co-authored by Zack Kayyali and Hicham (he-sham) Mourad
The steps below detail how to install Ansible Automation Platform on AWS United States GovCloud from the AWS Marketplace. The steps to deploy into AWS GovCloud and AWS Commercial cloud are nearly identical. Before starting your deployment process, please ensure the AWS account you are using to deploy has the following IAM roles. These IAM roles are required to deploy the AWS foundation stack offering. The foundation stack offering here refers to the base Ansible Automation Platform 2 deployment.
This blog details how to deploy Ansible Automation Platform on AWS and access the application. This deployment process will be configured to set up Ansible Automation Platform in its own Virtual Private Cloud (VPC) that it creates and manages. We also support deploying into an existing VPC.
To begin, first log into your Commercial AWS account. If you have a private offer, ensure that these are accepted for both the foundation and extension node offerings.
Note:

Welcome to the Ansible Lightspeed with IBM Watson Code Assistant Technical Preview
By Craig Brandt
At Red Hat Summit and AnsibleFest 2023, we announced Ansible Lightspeed with IBM Watson Code Assistant, a new generative AI service for Ansible automation. Today, we are thrilled to announce the Ansible Lightspeed technical preview launch.
In this blog, we’ll walk through the steps to access the Ansible Lightspeed with IBM Watson Code Assistant technical preview service and get it up and running in your Visual Studio Code environment. Then we’ll share more about what you can expect from the experience and how to generate your first Ansible tasks with generative AI.
This is exciting stuff, so let’s dive right in.
Ansible Lightspeed with IBM Watson Code Assistant is a purpose-built generative AI tool that aims to streamline the creation of Ansible content. This capability is natively integrated into your VS Code editor via the Ansible VS Code extension. The AI capabilities are powered by Watson Code Assistant, a foundation model trained on Ansible Galaxy, GitHub, and other open sources of data.
The technical preview is open and available, free of charge, to all Ansible users. As more users engage with Continue reading
Cisco announces AI Networking versions of SIlicon One ASICs and buys another DEM business. HPE Greenlake adds AI LLM. FTC talks bandwidth caps. Google accusing Microsoft of monopolistic behaviour. We laughed.
The post NB436: Cisco AI Silicon, DEM. HPE Greenlake AI LLM. FCC Talks Bandwidth Caps. appeared first on Packet Pushers.
At Red Hat Summit and AnsibleFest 2023, we announced Ansible Lightspeed with IBM Watson Code Assistant, a new generative AI service for Ansible automation. Today, we are thrilled to announce the Ansible Lightspeed technical preview launch.
In this blog, we'll walk through the steps to access the Ansible Lightspeed with IBM Watson Code Assistant technical preview service and get it up and running in your Visual Studio Code environment. Then we'll share more about what you can expect from the experience and how to generate your first Ansible tasks with generative AI.
This is exciting stuff, so let's dive right in.
Ansible Lightspeed with IBM Watson Code Assistant is a purpose-built generative AI tool that aims to streamline the creation of Ansible content. This capability is natively integrated into your VS Code editor via the Ansible VS Code extension. The AI capabilities are powered by Watson Code Assistant, a foundation model trained on Ansible Galaxy, GitHub, and other open sources of data.
The technical preview is open and available, free of charge, to all Ansible users. As more users engage with Ansible Lightspeed, the Continue reading
Ignas Bagdonas sent a phenomenal summary of recent BGP developments to the RIPE Routing WG mailing list. Enjoy!
Found an interesting article describing the shenanigans of a biotech startup. Admittedly, it has nothing to do with networking apart from the closing paragraph…
But people will find all sorts of ways to believe what they want to believe, to avoid hearing things that they don’t want to hear, and to avoid thinking about things that are too worrisome to contemplate.
… which is a perfect description of why people believe in centralized control planes, flow-based forwarding, or long-distance vMotion.
Because you may not have many months to set up a proper security implementation for your Kubernetes environment, this blog post will go over a few key security implementations that you can get done in 2-4 weeks depending on team size.
The post Pods, Plans & Policies: Top Five Tips For Kubernetes Security appeared first on Packet Pushers.